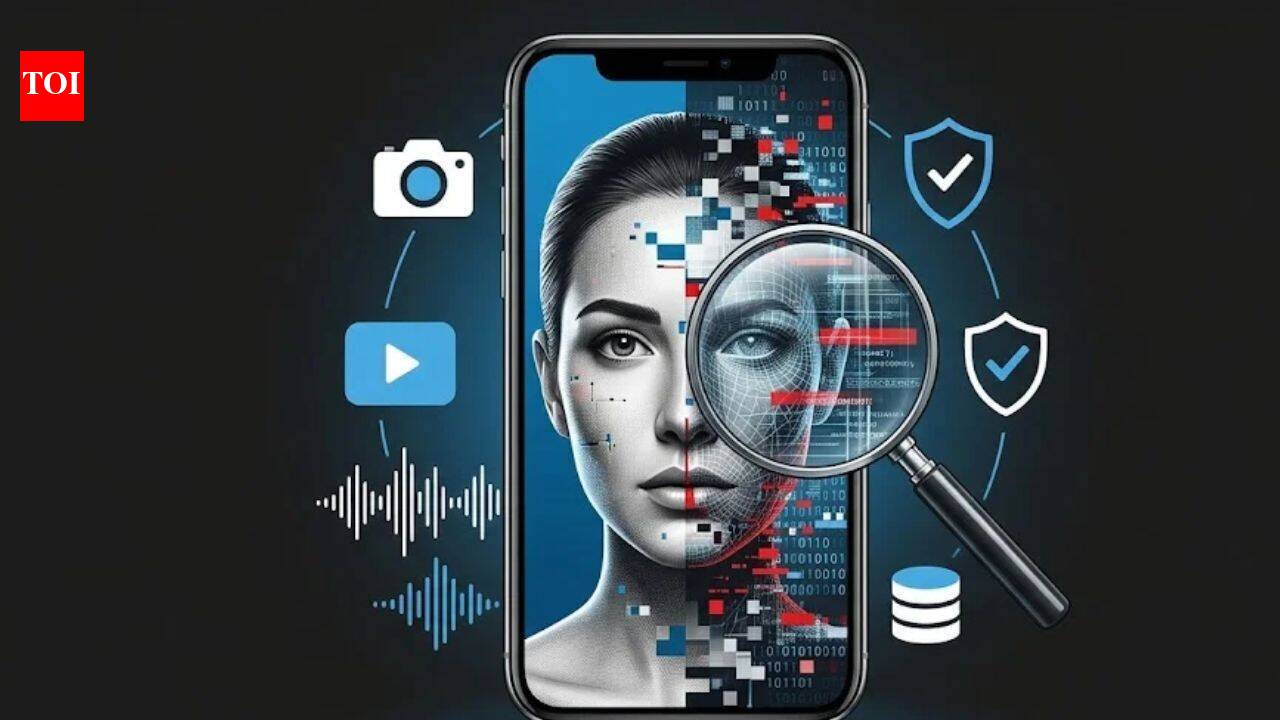
For most of modern history, people have lived by a simple rule: seeing is believing. A photograph was evidence that an event took place. A video was proof that someone said something. A familiar voice on the phone was enough to confirm that the person on the other end was who they claimed to be. These assumptions have guided how we understand news, how we trust one another, and how we make decisions in everyday life. But artificial intelligence has quietly changed all of that. Today, AI can create videos of people saying things they never said, clone a person’s voice from a short recording, and generate realistic photographs of events that never happened. In a world where information travels around the globe in seconds, it has become increasingly difficult to separate what is real from what is fabricated. Recent incidents show that this is not just a technical problem for experts to worry about. It is a threat to personal safety, democratic freedom, journalistic credibility, and public trust. We have reached a turning point where ordinary people must learn a new skill: verifying what they see and hear before trusting it. The old assumption that seeing is believing no longer holds. Instead, we must adopt a more cautious mindset—one that asks questions, checks sources, and refuses to accept media at face value.
One of the most striking examples of this new reality came in November 2023, when a manipulated video of Indian actress Rashmika Mandanna went viral across social media. The original video had been posted in early October by a social media personality named Zara Patel. It showed Patel in an elevator, but a version of the clip had been altered using AI to replace her face with Mandanna’s. The result was a deepfake so convincing that countless viewers believed they were watching the actress herself. Within days, the video had been shared widely, and by November 10, the Delhi Police had registered a case and begun investigating how the video had been circulated. The incident sparked outrage and fear, not only because it targeted a public figure, but because it showed how easily anyone could be falsely portrayed in a video without their knowledge or consent. Mandanna herself spoke out about the violation, highlighting the deep anxiety that comes from losing control of your own image. The episode was a wake-up call: if a high-profile actress could be seamlessly placed into a video she never appeared in, then every ordinary person is vulnerable too. Deepfake technology does not discriminate. It can be used to humiliate, defame, and harass, and its victims are not just celebrities but also students, ordinary workers, and family members. The Rashmika Mandanna case demonstrated that privacy is no longer something we can take for granted in the digital age. It showed that a person’s face and identity can be stolen, manipulated, and weaponized in a matter of days, and that the damage can spread faster than the truth can catch up.
Just a few months later, in March 2024, a mother in Khargone, Madhya Pradesh, received a terrifying phone call. The caller said her daughter had been kidnapped and demanded three lakh rupees in ransom. What made the call particularly horrifying was that the voice on the other end sounded exactly like her daughter’s. The frightened mother, convinced she was hearing her child’s desperate voice, transferred fifty thousand rupees before she could confirm what was happening. In reality, her daughter was safe in her hostel. The kidnapper was a scammer using AI voice-cloning technology to imitate the young woman’s voice. This incident reveals something deeply unsettling: hearing is no longer believing. Our ears, like our eyes, can now be deceived. Voice-cloning tools have become so advanced that they can replicate a person’s unique speech patterns, tone, and emotional nuances using only a small sample of audio. For scammers, this opens up a dangerous new world of possibilities. They can impersonate a family member in distress, a boss asking for a favor, or a trusted official requesting sensitive information. The emotional impact on victims is profound, because the deception is so personal. It strips away the basic trust we rely on when we hear the voice of a loved one. The Khargone incident is not an isolated case. Similar scams have been reported around the world, targeting vulnerable people, especially the elderly, by exploiting their natural instinct to help when someone they love is in trouble. The lesson is clear: even the most familiar voice must be verified when the request is urgent, unusual, or financial.
The same technology that deceived a mother and harmed an actress has also been used to create false public endorsements involving top government officials. In November 2024, a manipulated video circulated online supposedly showing Finance Minister Nirmala Sitharaman and Reserve Bank of India Governor Shaktikanta Das promoting an investment scheme. The video used altered footage and AI-generated audio to make it appear as though the officials were praising a fraudulent plan that promised unrealistic financial returns. Many viewers, trusting the authority and credibility of the officials’ images, could have been easily misled into investing their hard-earned money. Fact-checkers quickly established that neither official had ever endorsed the scheme, but by that point the video had already reached a wide audience. This incident is especially dangerous because it combines two powerful tools: the public’s trust in respected figures and the deceptive power of AI. Fraudsters understand that people are more likely to believe a fake message if it comes from someone they admire and trust. By hijacking the faces and voices of leaders, celebrities, and experts, they can make fraudulent schemes look legitimate. The Sitharaman case also demonstrates how AI-generated content can blur the line between journalism and manipulation. A video like this can be shared thousands of times, reported on by well-meaning users, and believed by people who would never normally fall for an online scam. It undermines faith in genuine government announcements and makes it harder for citizens to know what their leaders actually said. When public figures can be made to say anything, truth itself becomes a casualty.
These three incidents are just a glimpse into the broader problem of digital deception. AI-generated videos, or deepfakes, can make political leaders appear to make controversial statements, actors appear in films they never joined, and ordinary people appear to perform acts they never committed. Fake news spreads rapidly on social media, often outpacing the truth because sensational headlines and emotionally charged content naturally attract more attention. Even genuine photos and videos can be manipulated simply by removing context, editing a few frames, or pairing them with false captions. Meanwhile, voice-cloning scams continue to grow more sophisticated, allowing criminals to impersonate anyone from a grandchild to a company executive. The result is a digital landscape where nothing can be accepted without question. But this does not mean we should become paranoid or distrust everything we see online. Instead, we need to build stronger habits of verification. Before trusting a shocking video, we can check whether it comes from a reputable source. We can search for the original publisher and see whether established news organizations have covered the same story. We can look for inconsistencies in lighting, lip movement, shadows, and audio quality, though we must remember that modern deepfakes are increasingly difficult to spot with the naked eye. We can use reverse image searches to see if a photo has appeared in a different context in the past. We can read beyond the headline and resist the urge to share something merely because it makes us angry or afraid. And if we receive an urgent call from a loved one asking for money, we can hang up and call them back on a known phone number before taking any action.
Ultimately, the burden of protecting the truth does not fall only on individual users. Social media platforms must do more to detect manipulated content, label AI-generated media, and provide clear information about the origins of images and audio. They should work with independent fact-checkers, act quickly when misinformation is reported, and make their recommendation algorithms more transparent so that misleading content is not endlessly promoted. Governments and technology companies also have a role to play, through regulations and tools that make it harder to use AI for malicious purposes while still allowing innovation and creativity to flourish. News organizations must continue to verify what they publish and explain to their audiences how they know something is true. But in the end, each of us must take personal responsibility for what we believe and share. In an age when seeing is no longer believing and hearing can no longer be trusted, critical thinking has become one of our most essential survival skills. We do not need to abandon trust altogether, but we must learn to trust with verification. We must give ourselves time to pause, to question, and to confirm. The technology that enables deception also gives us the tools to detect it, if only we are willing to use them. By combining cautious observation with independent checking, we can protect ourselves, our families, and our communities. We can keep the truth alive, not by refusing to believe anything, but by refusing to believe blindly. Trust, but verify. That is the new rule for living in a world where artificial intelligence can make anyone say anything, and where the line between real and fake is only going to keep blurring.