On October 29, 2026, the cryptocurrency world woke up to news that felt almost impossible: roughly $6.3 billion had been stolen from Binance, making it the largest crypto heist on record. Withdrawals were paused. Millions of users went from an ordinary day to an anxious refresh of their balances, hoping that their life savings, business funds, or long-term holdings were still there. That kind of collective alarm is not just a security problem; it is an emotional event. And where there is emotion, there are scammers. They wait for exactly this state of panic, when fear makes people click first and think later. Their entire strategy is to sound like Binance at the right moment, and they do not need a complicated attack to succeed. A familiar logo, an urgent subject line, a phone number that looks official, and a countdown can push a worried person past every normal safeguard. The tricks described below are the ones that usually appear after big exchange incidents. They are typical patterns, not reports of specific campaigns, so no one can predict every variation that may be circulating this week. If you want the technical story of the attack itself, it is covered in our Binance hack report. This article, however, is not about making you more afraid. It is about giving you a calm, clear set of warning signs, because the single best defense against a panic-driven scam is a slow, grounded checklist. When your money is at stake, you are allowed to pause. You are allowed to hang up. You are allowed to ignore a message that screams urgency. The people trying to steal from you are counting on the opposite. They want you to hurry, to trust the familiar logo, to believe that one small step will keep your account safe. Remember that the real Binance has entire teams working on reopening withdrawals and securing accounts. They are not racing you to a fake portal. They do not need you to act in the next ten minutes. If an offer or warning makes your heart race, that is exactly the effect to be suspicious of.
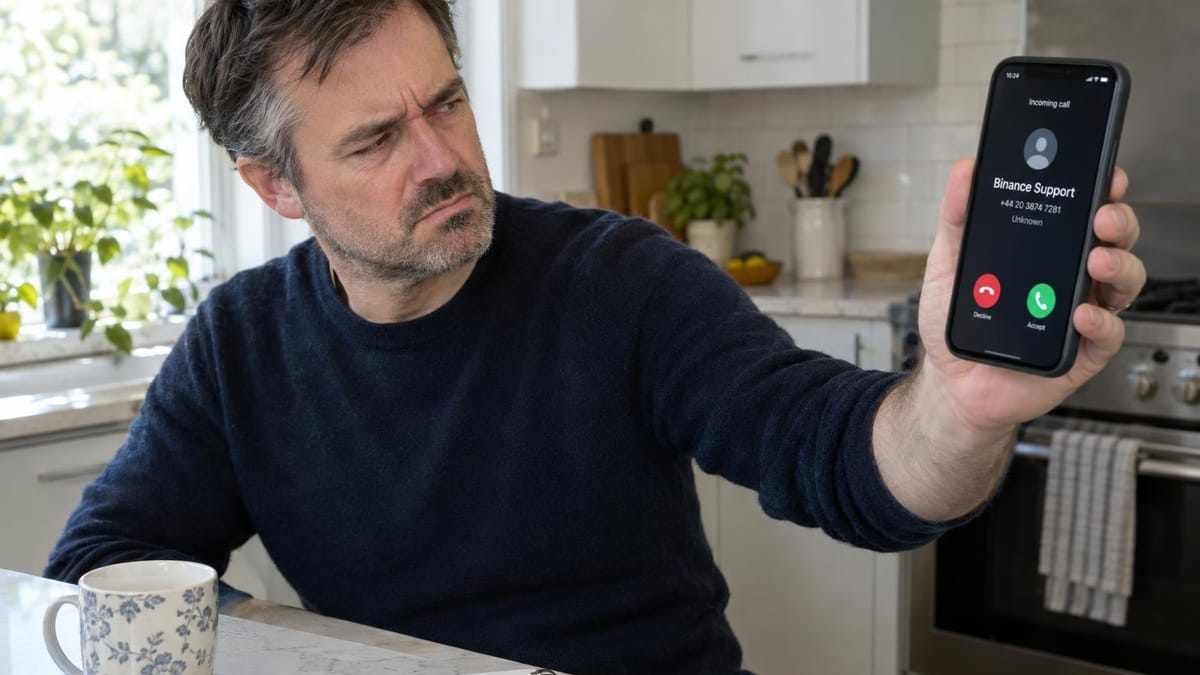
The most common trick is a message that appears to come from Binance security. It arrives by email with a Binance logo, by SMS, through Telegram or WhatsApp, as a reply under your post on X, or even as a phone call from someone who knows your name. The story is almost always the same: your account was “affected by the breach” and must be “verified,” “moved,” or “unlocked” before it is too late. The caller or message will sound confident, sometimes even sympathetic. They may mention the hack, refer to a transaction you do not remember, or tell you that a withdrawal attempt was blocked. The goal, however, is always the same: your login details, your two-factor authentication code, or permission to install a remote-access app on your device. If you give up any of those, you are not protecting your account; you are opening the door. How do you spot it? Start with a simple rule: Binance support does not contact you first about the hack. With millions of users, they cannot individually call or message everyone; official updates come through their own app and website. Binance also never asks for your password, your 2FA codes, or your seed phrase. Never. Not on the phone, not in email, not in a DM. If you have set an anti-phishing code in your security settings, genuine Binance emails will show it. A missing code is a red flag. If a caller asks you to read out a code that just arrived on your phone, understand what that code is: the key to your account. They are using you to complete the login they could not complete themselves. Hang up. Delete the message. Do not reply. If you are still worried, open the official Binance app from your phone’s home screen and look at your own security settings. That is the only source you can trust in that moment. No legitimate support person will ever ask for the same secrets that would let them steal from you. If they need to verify you, they have other ways that do not involve your password or a live code.
Binance has said it will cover every loss. Scammers turn that promise into bait. Expect paid ads, social media posts, and emails linking to pages that offer a “compensation claim,” a “refund portal,” or a “SAFU payout.” The page will look polished. It may have the Binance logo, a countdown timer, a customer support widget, and a field asking you to log in with your Binance details. The moment you type your email and password, those details go straight to the scammer. Other versions ask you to connect a crypto wallet and sign a request with your wallet. Signing may look harmless, but it can give a drainer permission to empty the wallet, the same mechanism used in fake airdrops like the Rabby airdrop scam. The scam works because it combines good news with a technical action: people want to believe they are being made whole, and they do not want to miss their share of the refund. How do you spot it? There is nothing to claim through outside pages. Period. Any official step from Binance will appear inside its own app and on the website that you type into your browser yourself, not through a link in a message. A page that asks for your wallet signature, a fee, or your seed phrase to “release” a refund is fake. The real process would never require you to spend money or expose your private keys. If you are unsure, go directly to binance.com or to the app store on your phone, and check the announcements section. If the information is not there, it is not real. Think of it this way: a stranger standing outside a bank who offers to recover your lost deposit faster if you hand over your ATM card and PIN is not a helper. He is a thief. The same logic applies online, and the only difference is that the stolen money leaves without a sound.
After every large theft, “crypto recovery experts” appear. They show up in search ads, in comment sections, in private messages, and on Telegram channels. Their pitch is simple: for an upfront fee, they can trace your lost funds and return them. They may show screenshots of past recoveries or claim to have special contacts inside Binance, law enforcement, or stablecoin issuers. In this case, the offer makes even less sense than usual, because Binance has said it will cover user losses itself. Why would you pay a stranger to recover money that the exchange has already promised to restore? The tracing and freezing that actually happens after a hack is done by blockchain analysts, stablecoin issuers, and law enforcement, and they work through official channels, not through a voice note from someone who found your email address. Paying a recovery service usually means losing money twice. The pattern is identical to fake refund offers in tech support scams: first they scare you, then they promise to rescue you, then they ask for a “small” payment, then they disappear. Alongside this, scammers are also exploiting the news that withdrawals may reopen soon. Reuters reports that Binance expects to resume withdrawals within about 45 hours. That timetable creates a countdown in people’s minds. Scammers know this. Expect fake announcements with a link and a deadline, such as “withdraw within 2 hours or your balance will be frozen again.” The link leads to a copy of the Binance login page. If you fall for it, you have just handed over your credentials to the same people who may have been involved in the original theft. When withdrawals really reopen, you will see it in the official app without clicking anything. No legitimate announcement will ask you to verify anything before you can access your own money. Patience is your armor.
Let’s make one thing absolutely clear: there are certain things Binance never asks for. Your password or your 2FA codes, whether by phone, chat, email, or form. Your seed phrase or private keys, ever. A fee, a deposit, or a “gas payment” to release frozen funds or a refund. Installing remote-access software such as AnyDesk or TeamViewer. And moving your funds to a “safe wallet” address that someone sends you. Anyone who asks for one of these is not Binance. No exception, no special case, no “security partner,” no “government agent.” The people behind the attack, which analysts link to North Korea’s TraderTraitor unit, went after the people and systems with access to money. They used deception, technical skill, and targeting to reach their goal. Small-time scammers are doing the same thing to users, only through a phone call or a fake page. They are not less dangerous because they are less sophisticated. They are just easier to spot if you know the list. Keep this list somewhere you can find it: on your phone, in a note, on your desk. If a message contains any of these requests, you can stop reading. You do not need to analyze the tone, the logo, or the grammar. One request for a password or a seed phrase is enough. The rest is noise. And if you are worried that ignoring a genuine warning will make things worse, remember that real security messages from Binance are not desperate. They do not ask for secrets. They do not rush you. They do not tell you to download a program. They point you to your own account settings and let you make the next move. That is the difference between a company protecting you and a scammer chasing you. If someone contacts you with an emergency, ask yourself: if this were true, would the real company need me to act without thinking? The answer is no.
If you meet a scam, the worst thing you can do is handle it quietly and alone. Report fake messages and pages to Binance through the official app. You can also report fraud to the authorities where you live, such as the FBI’s IC3 in the United States or Action Fraud in the United Kingdom. Report fake profiles and ads to the platform where you saw them; social media companies can take down accounts and help stop the next victim. If you already gave away a password or a 2FA code, do not spend time blaming yourself. Change both from a trusted device, not from the device where you may have clicked a malicious link, and check your account as described in our checklist for Binance users. If you signed a request in your own wallet, revoke the approvals immediately and move the remaining funds to a new wallet that was never connected to that request. Time matters, but speed without care can make things worse. Work through the checklist one step at a time. If you are not sure how to revoke a wallet approval, search Binance’s official guides or talk to a trusted person who understands crypto. The most important thing is to break the cycle of panic. Scammers rely on shame, silence, and speed. You can defeat all three by slowing down, telling someone, and verifying from official sources. This hack has been a painful event in the history of cryptocurrency, and it is natural to feel shaken. But you are still here, and you still have choices. The next time a message appears with a Binance logo and a warning, let your first thought be: I will not act from fear. I will check the official app. I will not share my passwords. I will not pay a stranger to save me. That small set of habits is more powerful than any scammer’s script. Breathe, verify, and then act. You are not being paranoid; you are being careful. And in moments like this, careful is exactly what you need to be.