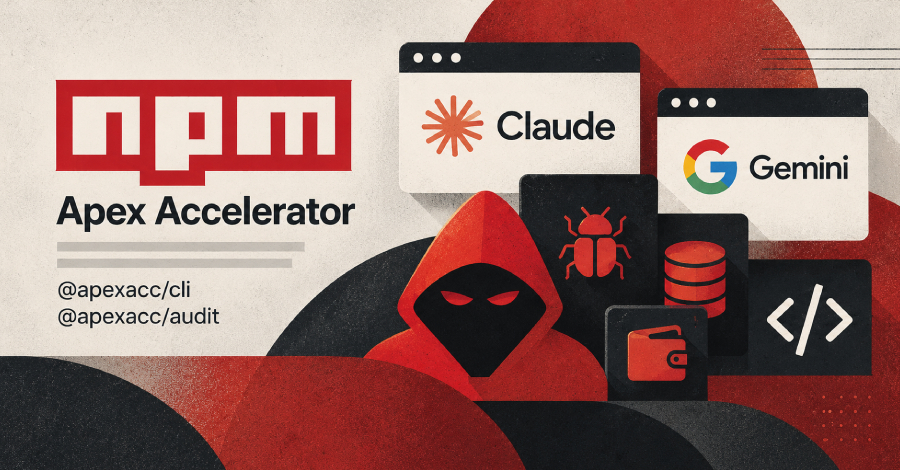
Picture this: you’re a crypto startup founder, and out of nowhere an “accelerator” messages you with an offer that sounds too good to resist. Free AI credits for Anthropic’s Claude and Google’s Gemini, helpful coding tools, even a security audit that promises to keep your project safe. The only catch is that the “gift” is actually a trap. Security researchers at Elastic Security Labs recently uncovered a fake Web3 accelerator called Apex Accelerator that has been handing out malicious npm packages to Windows and macOS users. These packages don’t just fail to deliver their promised features; they quietly install information-stealing malware and backdoors. The operation, tracked as REF8801, was aimed squarely at cryptocurrency startups and founders, and it shows just how creative attackers have become at weaponizing trust. Instead of breaking in through a vulnerability, they didn’t have to exploit anything at all—they simply offered free stuff, and people installed the danger themselves. The researchers noted that the tools delivered information-stealing malware and backdoors for both major operating systems, while also repackaging a legitimate coding agent to send model requests through attacker-controlled services. As if that weren’t enough, the fake audit tools generated fabricated security findings, making victims think their projects were being checked when the malware was really checking them out for theft.
The whole operation was built on a carefully constructed illusion of legitimacy. The attackers posed as a venture capital entity called Apex Accelerator, complete with a website, social media presence, and even appearances at major events like TOKEN2049 in Singapore. According to Internet Archive snapshots dating back to March 19, 2026, the Apex Foundation promised investments of $235,000, along with grants and partnerships, and claimed it would connect projects with venture capitalists, angel investors, and private equity firms—unless, of course, the projects didn’t meet their criteria. That kind of language is designed to make a fake fund look selective and serious. The group also reached out to cryptocurrency wallet developers and builders of market intelligence tools on social media, offering direct investment and asking them to run a “due diligence tool” called @apexacc/cli. Anyone familiar with crypto knows that being courted by an investor feels like validation, and that emotional pull can override caution. The masks were layered: npm packages were published under the username “apexaccelerator,” linked to a GitHub account called “apexaccs,” and tied to something called the Apex Foundation. Two of the main packages were @apexacc/cli, advertised as an “AI advisor for Web3 founders” powered by Claude Fable 5 and Gemini 2.5 Flash, and @apexacc/audit, a so-called Web3 Security Scanner that claimed to offer 18 tools for doing your own research and auditing smart contracts. Interestingly, this wasn’t even the first time the group had struck. In late July 2026, SafeDep had already detailed three other npm packages connected to the same campaign—@apexfdn/apex, @copilot-mcp/apex, and @apexfdn/copilot-mcp—which were caught distributing a macOS stealer belonging to the Atomic Stealer family, also known as AMOS. The Apex Foundation was linked to at least two distinct domains since April 2026: apexaccs[.]org and apexfdn[.]xyz. Elastic also noticed Russian-language comments in the source code commit history, but that clue alone isn’t enough to definitively identify who was behind the operation. It could be a deliberate misdirection or simply the language of the developers, but either way, the attackers clearly invested time in making themselves look like a real, credible venture fund.
What happens after installation is the real nightmare, because none of the promised features actually work. The 18 security tools inside @apexacc/audit generate fabricated findings, meaning they produce reports that look serious but are completely made up. Meanwhile, @apexacc/cli’s scoring test returns an “unsupported assessment” of a project that doesn’t even exist. These fake functions are just cover stories. In reality, both packages act as launchpads for malware. When a victim runs the package, it first phones home to a verification server at vrf.apexaccs[.]org with a simple HTTP POST request that says either “win32” or “darwin,” depending on the operating system. That server then tells the package which malicious payload to fetch. For Windows victims, the infection chain is especially elaborate. The malware retrieves a Base64-encoded PowerShell command, which contacts another endpoint at 0auth-chromium[.]com/APIService to grab a second PowerShell script called drop.ps1. That script downloads an executable named bludness.exe from ehegisnightmare[.]icu and launches it in a hidden window. This is a Python loader built with PyInstaller, and it checks whether it already has administrator privileges. If it does, it immediately downloads the next stage from ehegisnightmare[.]icu, saves it as %TEMP%exegis.exe, and runs it. If it doesn’t have admin rights, it tries to bypass Windows User Account Control using a well-known privilege escalation technique called UACME’s ucmDebugObjectMethod(). The next file, exegis.exe, is another Python-built loader that collects system metadata and running processes, performs anti-virtual-machine checks to avoid being analyzed by security researchers, and then decrypts and launches yet another bundled loader as %TEMP%updater_loader.exe. That final loader is a Golang executable that patches important Windows security mechanisms such as Antimalware Scan Interface and Event Tracing for Windows, unhooks ntdll.dll to blind endpoint security tools, and then loads the ultimate payload—shellcode—directly into its own memory. That shellcode is a native information stealer. It checks for signs of a prior infection, then harvests system information, clipboard text, process listings, Wi-Fi profile names, screenshots, and data from wallets, browser extensions, messengers, remote-access and FTP applications, VPN clients, browsers like Chrome, Edge, Firefox, and Yandex, and even game clients. It can also bypass Chrome’s app-bound encryption protections to extract saved passwords, session cookies, browsing history, download records, and profile metadata. All of that stolen data is then exfiltrated through Telegram, which is both casual and frightening—the attackers are using a messaging app as their command-and-control channel.
Mac users are not spared, either. The macOS infection chain begins when the package downloads a remotely hosted bash script and runs it on the machine. That script then pulls down a GZIP-compressed archive from verify.apexfdn[.]xyz/unix/, saves it as package.tar.gz in a temporary directory, and extracts it. Inside the archive is a dropper for a macOS backdoor called CloudSyncD. This backdoor tries a particularly user-friendly trick: it displays a fake authorization prompt asking for the victim’s system login password. If the victim falls for it and types their password, the malware uses those credentials to launch an embedded payload with sudo privileges, meaning it gets full control over the system. Once running, the payload performs host discovery, collects hardware and operating-system details, and contacts an external server at ccmihr[.]com to transmit that data and receive further instructions. That server can then tell the malware to download and run additional payloads, giving the attackers a persistent foothold on the victim’s machine. If this all sounds familiar, that’s because CloudSyncD was previously documented by Jamf Threat Labs, which found it being distributed through a fake Zoom installer. The malware was detected in the wild in mid-September 2026. What makes this particularly interesting is how the macOS malware is evolving. As Jamf researchers noted, this backdoor illustrates how macOS malware continues to move toward native implementations, string protection, and execution paths that avoid writing payloads to disk, while still relying on the oldest social engineering trick in the book: asking the user for their password. It’s a weird mix of advanced technical sophistication and old-fashioned psychological manipulation. The entire infection is designed to be quiet and avoid detection, but it still needs that moment of human trust to succeed. And that’s exactly what makes it so dangerous. No amount of antivirus software can help if a user willingly types their password into a fake prompt the malware created.
Once the malware is in place, the data theft is broad and invasive. On Windows, the final stealer payload is a digital pickpocket on steroids. It vacuums up saved passwords and cookies from major browsers, including Google Chrome, Microsoft Edge, Mozilla Firefox, and Yandex. It can bypass Chrome’s app-bound encryption, which was specifically designed to stop this kind of theft, and steal session cookies, browsing history, download records, and profile metadata. It also targets cryptocurrency wallets, browser extensions, messaging apps, remote access tools, FTP clients, VPN software, and game clients. The stealer collects Wi-Fi profile names, captures screenshots, reads clipboard contents, and lists running processes to understand what kind of machine it’s sitting on. All of this information is then sent to the attackers via Telegram, a simple and surprisingly effective way to exfiltrate data without setting up a complex command-and-control infrastructure. On macOS, CloudSyncD is just as dangerous. It can perform host discovery to map out the local network, gather hardware and OS details, and then wait for commands from its control server. That means the attackers can use the infected Mac as a remote-controlled tool, pushing new malware or stealing more data at any time. The goal for both platforms is the same: learn as much as possible about the victim, steal anything valuable, and stay hidden as long as possible. The sheer scope of the data collection is a reminder that these attacks aren’t targeted at random individuals—they’re aimed at people who work in crypto, an industry where a single compromised wallet or leaked private key can result in enormous financial loss. The attackers aren’t just hoping to steal something; they’re planning to empty digital bank accounts, hijack identities, and maybe even manipulate the victim’s business decisions.
Perhaps the most unsettling part of this entire campaign, though, is how it targets artificial intelligence tools. The malicious packages don’t just steal passwords and files—they also intercept and redirect traffic sent to OpenRouter, a service that lets developers access large language models. If a victim uses the fake AI assistant or something connected to it, the package can reroute their LLM requests through attacker-controlled servers. Worse, it registers an MCP server—a Model Context Protocol server—under the attacker’s control in the victim’s agent configuration. This gives the attacker a front-row seat to everything the AI agent sees and does. Prompts, conversation history, code snippets, and tool outputs are all sent to the attacker’s API instead of the legitimate service. And the attacker’s MCP server can also inject instructions directly into the agent’s prompt, along with fake tool names, descriptions, and accepted inputs. These injected instructions don’t just confuse the model; they can actually influence its decisions. The AI agent might be tricked into running commands, revealing information, or making choices that benefit the attacker, all while the user believes they are getting help from an AI-powered advisor. That’s a terrifying escalation. It means attackers are no longer just stealing credentials; they’re hijacking the decision-making process itself. For a crypto founder using an AI agent for due diligence or code review, that could lead to approving a dangerous contract, sending funds to the wrong address, or revealing sensitive business plans to someone listening on the other side. The entire campaign is a reminder that in the world of blockchain and Web3, trust itself has become a vulnerability. The Apex Accelerator story shows how easily legitimate-looking tools can be weaponized, and how important it is to question free offers, verify identities, and treat every “security audit” as something that needs to be audited itself. Sometimes the most valuable security tool is plain skepticism.