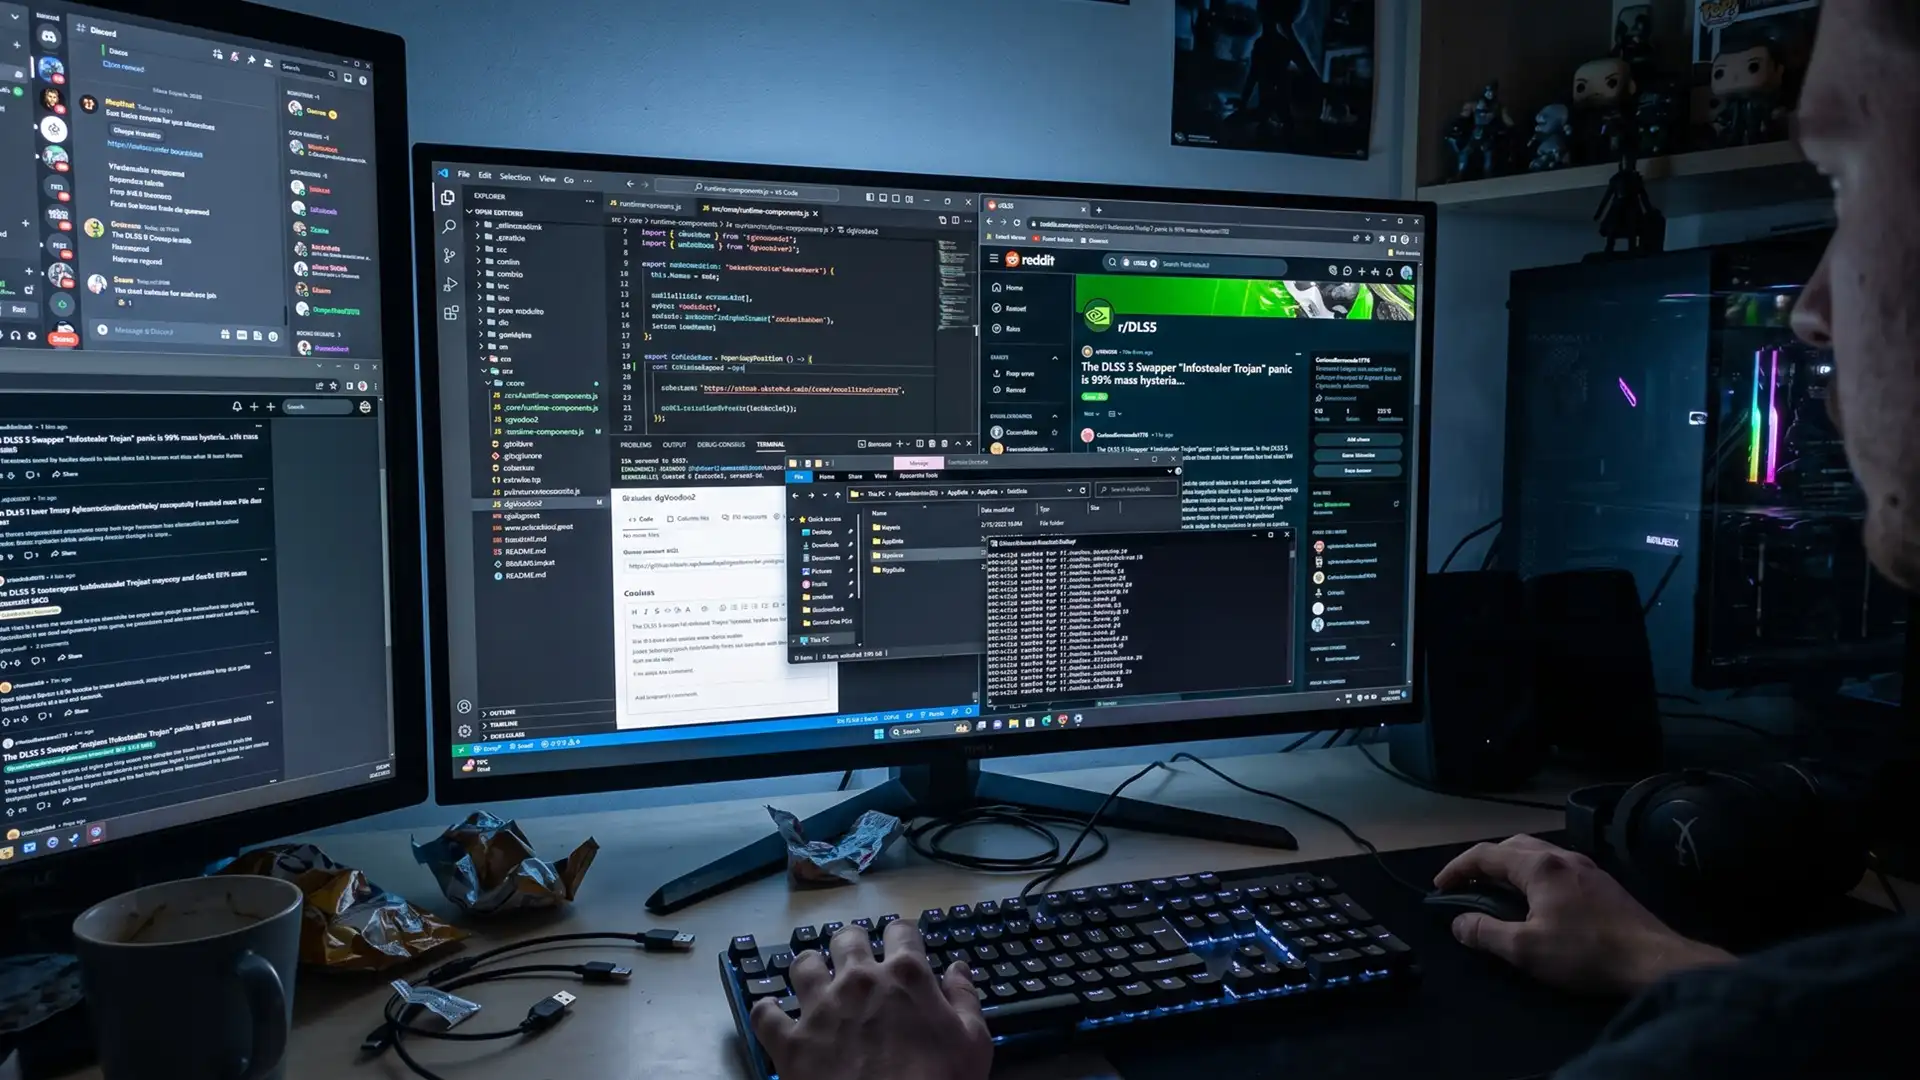
One small article, 241 views, and a wildfire of panic. On October 19, 2026, Atremis Volosh published a story that, despite its modest reach, managed to send shockwaves through the gaming community. The subject was DLSS 5 Swapper, a third-party utility built by a developer known as rakanki911. According to the reports, GitHub had blocked the project’s repository because the utility supposedly contained a built-in stealer. This wasn’t just some vague threat; the accusations said the software was downloading a malicious archive called dgoodoo-2.8.7.zip.part. For PC gamers, that combination of words was enough to trigger immediate alarm. Many had been using the Swapper to get the most out of DLSS 5, a state-of-the-art AI-driven upscaling technology. DLSS 5 uses neural rendering to generate photorealistic lighting, materials, and fine details in real time, and its arrival had already been a major talking point in the gaming world. The Swapper made it easy to switch between different versions of the upscaler, and the idea that a tool so many people trusted could be hiding a malware drop felt like a betrayal. The reaction was swift and visceral. People began formatting their drives, resetting Windows installations, changing every password they could think of, and even warning friends to avoid the entire DLSS ecosystem. In some communities, the story escalated to the point where people were convinced that the tool had been compromised for months. But the panic, as it turns out, was built on a series of misread signs and false assumptions. Once independent researchers actually looked under the hood, the story began to fall apart in spectacular fashion. The tool was safe. The accusations were unfounded. And the only real damage, ironically, was caused by the very people who tried to warn everyone about a threat that never existed.
Before diving into the technical details, it helps to understand why DLSS 5 Swapper mattered in the first place. Deep Learning Super Sampling, or DLSS, is NVIDIA’s AI-powered rendering technology that has become one of the most important features in modern PC gaming. The latest version, DLSS 5, pushes the concept significantly further by moving beyond simple upscaling into neural rendering. This means the AI doesn’t just boost resolution; it can predict and generate entire aspects of a scene, including photorealistic lighting, complex materials, and subtle details like hair and foliage. For gamers, this leads to massive frame rate improvements without sacrificing visual quality. However, the technology is constantly evolving, and different games sometimes work better with different versions of DLSS. That’s where the DLSS 5 Swapper came in. It allowed users to extract, replace, and manage DLSS binaries in their game directories, giving them greater control over performance and image quality. The utility was especially popular among enthusiasts who wanted to use the latest DLSS version in older games that had not yet received official updates. It was a niche but beloved tool. So when news broke that the Swapper had been blocked by GitHub for supposedly downloading malware, the reaction was not just fear but betrayal. A tool that represented progress and control over cutting-edge technology was now being painted as a security nightmare. Yet, the actual history of the utility showed no signs of malicious behavior. It had been used by thousands of people without incident. The sudden accusation seemed out of character, and that was one of the first clues that something was wrong with the story. In a world where supply chain attacks have become a real concern, however, even the most loyal users were willing to believe the worst. The truth, once uncovered, would reveal a much more mundane explanation.
The first serious cracks in the story appeared when independent analysts unpacked the utility and studied its behavior. What they found was a very different picture from the one painted by the panic. The file that had been identified as a malicious stealer was actually a legitimate library called dgVoodoo2. This is not a secret spy program or a hidden backdoor; it is a well-known compatibility layer used to run graphics applications on older versions of DirectX and other legacy graphics APIs. The strange name that appeared in the original report, dgoodoo-2.8.7.zip.part, was simply a typo. Someone had misspelled dgVoodoo2, and the error had taken on a life of its own. The extra .part extension also made sense the moment it was explained. Many download managers and runtimes use .part as a temporary suffix while a file is being streamed or downloaded. When the download is complete, the file is renamed to its final name. This is a standard practice, not a sign of malicious intent. The library was being fetched from the official repository maintained by the Dege developer, and it was verified using a SHA-256 cryptographic hash. That means the utility checked the file’s cryptographic signature against the expected value before using it. If the hash did not match, the file would be immediately deleted)Skip. This verification process completely eliminates the possibility of someone tampering with the download or swapping it out for a modified version. In other words, the very thing that looked like an attack was actually a carefully designed safety mechanism.
So what about the Windows Defender warning that had sent everyone into a frenzy? The alert, labeled Trojan:Win32/Kepavll!rfn, was triggered by standard heuristic analysis. Heuristic algorithms are designed to detect suspicious behavior based on patterns rather than known signatures. They are useful, but they are not perfect. The DLSS 5 Swapper injects DLL files into game processes. That is the whole point of a swap tool; it needs to load custom graphics libraries inside the game so that the selected DLSS version takes effect. However, DLL injection is exactly the kind of behavior that antivirus engines are trained to treat with suspicion. Malware often uses DLL injection to hijack processes or steal data, so security software frequently flags any unsigned software that performs similar operations. Gamers know this all too well. Many legitimate tools, including mod loaders, graphics tweakers, and reshade presets, set off false positives for the exact same reason. Windows Defender’s alert was not proof of malicious intent. It was a warning sign generated by a pattern-matching system that saw familiar behavior and arrived at a worst-case assumption. A digital signature would have reduced the likelihood of a false positive, but the developer of the Swapper had not signed the executable, which is very common in small, independent projects. Once this was understood, the warning made perfect sense. It was not a smoking gun. It was a false alarm triggered by an overzealous security mechanism, combined with the fact that the tool does exactly what it is supposed to do: it modifies game files and injects code. The community’s reaction, while natural, was based on a misunderstanding of how heuristics work.
The most thorough part of the investigation was a full code review. Researchers examined the utility’s source code from top to bottom, checking for any functionality that could collect user data, read cookies, or steal authorization tokens. They found nothing. There were no suspicious network connections, no hidden data exfiltration routines, and no attempt to access anything outside the scope of the tool’s stated function. Every network request made by the utility could be accounted for, and every single file it downloaded came from a legitimate source. The conclusion was clear: the DLSS 5 Swapper was safe. The entire situation had been the result of mass panic, amplified by social media and the natural fear that comes from seeing a scary filename combined with an antivirus alert. But there was another layer to the story. GitHub had blocked the repository, and many assumed this was because the project had been proven malicious. In reality, the block was triggered automatically by the platform’s moderation systems. When large numbers of frightened users reported the repository as malicious, the automated system responded by taking it offline. It was a textbook case of a report avalanche. No human reviewer had carefully examined the code and deemed it dangerous. The system simply saw overwhelming signals from users and followed its instructions. By the time the panic subsided ranking and the truth became clear, the damage had already been done. The developer’s reputation had been dragged through the mud, and many users had taken unnecessary steps to protect themselves. The repository was eventually restored, but the incident left a mark. It served as a reminder that platforms like GitHub rely on automated moderation tools that can be fooled by coordinated or panic-driven reports)Skip. The absence of human judgment in these systems is both a convenience and a vulnerability, and in this case, it allowed a harmless tool to be taken down by a wave of misinformation.
In the end, the DLSS 5 Swapper story is a lesson about how quickly fear can overtake facts in the digital age. Every accusation, from the supposed stealer to the bizarre filename, was explained by something simple and legitimate. The strange dgoodoo archive was a typo. The .part extension was a temporary download marker. The antivirus warning was a heuristic false positive. The GitHub block was an automated reaction to mass reporting. There was no conspiracy, no hidden agenda, and no threat to users’ data. But that doesn’t mean the panic was meaningless. It was a reminder of how fragile trust can be in the PC gaming community, and how easy it is for a single false report to spiral into something much larger. Thousands of people changed passwords and reinstalled operating systems because of a misunderstanding that was never verified before it went viral. The good news is that this story had a happy ending. The tool was cleared, the developer’s reputation was restored, and the gaming community learned something valuable about the importance of checking sources. The next time an alarming report appears, especially one that demands immediate action, it is worth pausing and asking a few basic questions. Is there an official source? Has anyone actually analyzed the code? Could there be a reasonable explanation for what looks dangerous? In an age of instant information, the ability to think critically is one of the most important tools we have. DLSS 5 Swapper may not have been a malware bomb, but the incident itself was a warning worth taking seriously, not about software, but about ourselves. We cannot afford to panic first and investigate later. The truth may not always be complicated; sometimes it is just buried under a pile of assumptions, typos, and unreadable filenames.