In early October, Ukrainian drone attacks struck data centers operated by Yandex, the Russian technology giant often described as “Russia’s Google.” Within hours, a familiar pattern of wartime rumor and speculation began to unfold across social media. Users claimed that the strikes had not only damaged physical infrastructure but had also disrupted, disabled, or even completely halted the activity of Russian propaganda bot networks. These bots, which are widely believed to spread disinformation, amplify Kremlin narratives, and manufacture fake online consensus, have become a notorious feature of the digital battlefield. The idea that a precision drone strike could somehow turn off an entire influence operation was always going to be compelling, and it spread with remarkable speed. It gained even more legitimacy when Ukrainian President Volodymyr Zelenskyy appeared to endorse the theory. Speaking at the Warsaw Security Forum, Zelenskyy suggested that the attacks on Yandex data centers had indeed reduced bot activity, saying that “there was less hate, less division, and fewer provocations [because] there were fewer bots.” For many people, this sounded like confirmation of what they had already suspected: that Ukraine had landed a direct blow not just on Russian infrastructure, but on the very machinery of Russian disinformation. However, as with so many viral claims in wartime, the full story is considerably more complicated, and the available evidence does not support the bold conclusions being drawn.
Zelenskyy’s office later walked back the president’s statement, at least to some degree. When BBC Verify asked for clarification, his office explained that he had not been talking specifically about bot activity at all. Instead, they said, he was “talking about the atmosphere on social media” and had seen “reports of fewer provocative and hateful comments” from many social media users. That distinction matters, because the shift from claiming that bots had been destroyed to claiming that the online mood had improved is a significant one. It is much harder to measure an “atmosphere” than it is to count automated accounts, and it is also much harder to prove that any change in that atmosphere was caused by a specific military action. So far, no clear evidence has emerged to link the Yandex strikes to a genuine decline in bot activity. Researchers who systematically monitor Russian disinformation campaigns have been explicitly skeptical of the narrative. Josef Holnburger, managing director of the Center for Monitoring, Analysis and Strategy, a German organization that tracks such operations, said that there is currently “no decline in Russian disinformation activities that could be explained by the attack on Yandex data centers.” That is a crucial statement, because it comes from people whose job is to watch these networks on a daily basis. If the bot armies had really been silenced or seriously degraded, they would likely be among the first to notice. The fact that they have not seen such a decline suggests that the connection between the drone strikes and the supposed disappearance of pro-Russian bots is more wishful thinking than established fact.
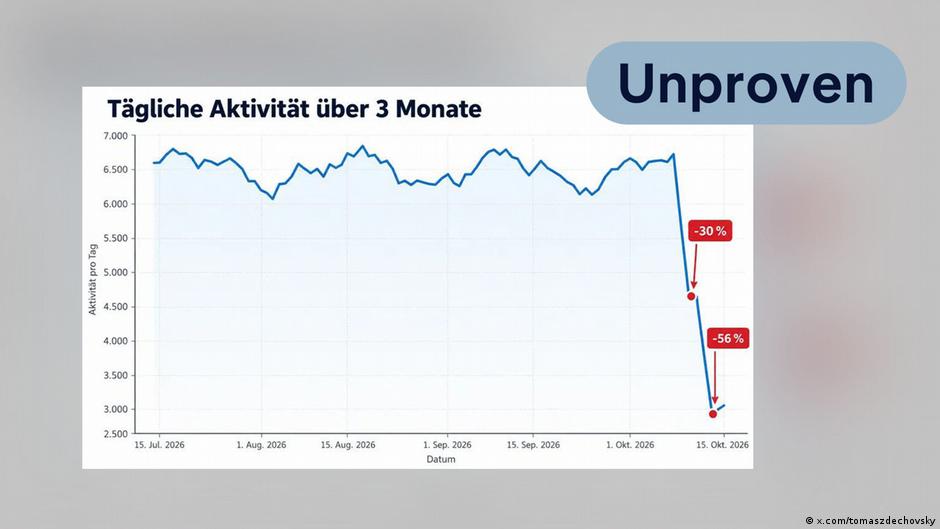
Still, in the absence of solid evidence, a misleading graph began to circulate online as supposed proof that the strikes had worked. The graph was shared by Tomáš Zdechovský, a Czech member of the European Parliament, and his post was viewed more than four million times on X. Zdechovský suggested that the graph might demonstrate a decline in “online activity around AfD,” the far-right German political party, although he did not specify exactly what kind of activity he meant. This vagueness should have been a red flag from the start. The graph, which was titled “Daily activity over 3 months” in German, appeared to show activity remaining relatively stable for most of the period before dropping sharply in early October, roughly around the same time as the attacks on Yandex data centers. To a casual viewer, that drop looked like a smoking gun. But a closer examination reveals that the graph may actually demonstrate nothing at all. There is no indication in the graph itself that the data has anything to do with AfD, or with German politics, or with Russian bots. The title is generic, the source is missing, and the methodology is completely unexplained. In other words, the graph relies entirely on the viewer’s willingness to fill in the blanks with their own assumptions. That is not how credible evidence works, and it is especially dangerous in an information environment already saturated with propaganda and counter-propaganda.
The technical problems with the graph are even more damaging to its credibility. For one thing, it is impossible to tell where the underlying data came from. No source is provided. There is no explanation of how the data was collected, which platforms were analyzed, or how the mysterious variable of “activity” was calculated. The numbers themselves are also strange: the activity level initially ranges between 6,000 and 7,000 before falling below 3,000, but the reader is never told what those numbers represent. Are they posts? Users? Comments? Interactions? No one knows. The graph also contains obvious scaling errors on both the X and Y axes. On the Y axis, the distance between 2,500 and 3,000 is smaller than the other 500-unit intervals, which distorts the visual representation of the data. Even worse, the Y axis does not begin at zero, a classic trick that makes declines look much more dramatic than they actually are. On the X axis, equal periods of time are represented by unequal distances, which further distorts the timeline. But perhaps the most glaring problem is the fact that the graph extends to October 15, with its final data point appearing to correspond to October 14. That would be unremarkable if the graph had appeared after that date, but it was first shared online on October 11. That means it contained data from dates that had not yet occurred at the time the graph was created. Data for future dates simply cannot exist. The graph was, in effect, predicting the future, which is a clear sign that it was not based on factual information and sound statistical methods. It might have been fabricated, it might have been carelessly assembled, or it might have been generated by an AI tool that filled in gaps with invented values, but whatever the explanation, it is not a reliable piece of evidence.
The possibility that AI was involved in creating the graph cannot be proven, but it also cannot be ruled out. The strange scaling errors, the lack of a clear source, and especially the apparent “hallucination” of future data all point in that direction. AI language models and image generators are known to produce plausible-looking outputs that fall apart under close inspection, and this graph fits that pattern uncomfortably well. Misleading and error-filled graphs, some of which may have been AI-generated, appear on social media with alarming regularity. German public broadcaster BR’s #Faktenfuchs team recently reported on a similar graph that falsely depicted industrial production in Germany, and it is likely that many other examples have gone unnoticed. The danger of these fake charts is that they lend an air of credibility to claims that would otherwise be dismissed. A graph looks scientific. It looks like someone did the research. It gives people a visual object to share and rally around, even when the data behind it is meaningless. In this case, the identity of the graph’s creator remains unknown, which only adds to the suspicion that it was not produced by a reputable researcher or institution. Yet despite all these red flags, the graph was viewed millions of times and helped reinforce a narrative that, however appealing, lacks evidentiary support.
Finally, there is the question of Cloudflare data, which is often cited in connection with claims of declining bot activity after the Yandex strikes. Cloudflare is a major internet infrastructure company that provides services to many websites, including security features that block traffic it assesses as non-human. Automated web traffic is extremely common and includes crawlers that scan websites for newly published content. Search engines, including Yandex itself, rely on these crawlers to index the web. Other bots are used for spam, scraping, and various other automated tasks. According to Josef Holnburger, however, there is a fundamental misunderstanding about what Cloudflare data actually shows. A decline in bot activity on websites, he argues, is something entirely different from a decline in inauthentic behavior by social bots on social networks. Looking at overall activity from Russian IP addresses on servers using Cloudflare services, Holnburger said there is no major decline in bot activity. Furthermore, there is no reason to assume that the infrastructure used by disinformation-related social bots would be hosted on Yandex data centers in the first place. These systems are more likely distributed across many different providers, precisely so that they can survive the kind of disruption that a single targeted attack might cause. In the end, the story of the Yandex attacks and the supposed death of Russian propaganda bots is a cautionary tale about the way information, misinformation, and wishful thinking can become tangled in times of war. It is understandable that people want to believe Ukraine’s military actions are having a direct impact on the information war. But the evidence so far does not support that conclusion, and the circulation of faulty graphs and misread data only makes it harder to understand what is actually happening. The truth, as usual, is messier than the narrative, and it requires patience, skepticism, and a willingness to resist the seduction of a satisfying story.