Think about how much trust we place in familiar names. When an employee opens a browser and searches for ChatGPT, Claude, or Microsoft Copilot, they are not looking for trouble—they are looking for help. They want to draft an email, summarize a document, write a bit of code, or create a marketing plan. In a matter of seconds, they click a link, download a file, or follow a set of instructions, all while believing they are using a legitimate product. That sense of trust has become one of the most dangerous vulnerabilities in modern business. Cybercriminals have noticed how deeply AI tools have woven themselves into daily work, and they are exploiting that reliance with growing confidence. Instead of building elaborate traps that require users to ignore warnings, attackers are simply impersonating the very brands employees already trust. They create counterfeit websites, fake installers, and bogus login pages that look remarkably like the real thing. According to recent research from ANY.RUN, these fake AI campaigns are not a niche or theoretical problem. They are actively targeting corporate users across industries, including developers, marketing professionals, and everyday employees who just want to use a helpful tool. The research paints a clear picture: attackers are using well-known AI names as camouflage, and by the time anyone realizes what happened, credentials are already stolen, malware is already running, and corporate systems are already compromised. The challenge for security leaders, then, is not just about blocking obvious malware anymore. It is about identifying threats hidden behind familiar application names and stopping them before a single click turns into a full-blown security incident. This is the new reality of AI adoption, and it demands a more human and more practical approach to security—one that acknowledges how people actually work, where they are most vulnerable, and how security teams can protect them without slowing down innovation.
The scale of the problem becomes clearer when you look at the numbers. Between April 15 and October 5, 2026, ANY.RUN researchers identified 1,258 public sandbox analyses linked to fake AI campaigns. That is more than a thousand instances where malicious files or URLs were actively analyzed because they were suspected of impersonating popular AI tools. The geographic distribution is telling. The United States accounted for 16% of submissions that included country information, placing it second only to India at 20%. But what is even more concerning is that US submissions led in two of the most significant campaign groups: fake Claude downloads and ChatGPT-themed attacks. This is not something happening only in distant corners of the internet. These attacks are landing on American businesses, and they are doing so in large numbers. The industry breakdown makes the threat even more universal. Technology appeared across all seven campaign queries examined by researchers, which makes sense given how deeply tech workers rely on AI tools. But the threat does not stop there. Telecommunications appeared in six campaign groups, education and consulting appeared in five each, and manufacturing, healthcare, government, and finance each appeared in four. It would be easy to assume that fake AI attacks only target software engineers or IT departments, but the evidence tells a different story. Whether an organization builds software, runs a hospital, manages public infrastructure, or handles financial transactions, its employees are exposed. In the United States, telecommunications and manufacturing stood out most frequently across the campaign queries. That means workers on factory floors, telecom network teams, and administrative staff are all being targeted through the same trusted AI brands. The takeaway for business leaders is sobering: if your company uses AI tools—and almost every company does now—then your employees are already in the crosshairs.
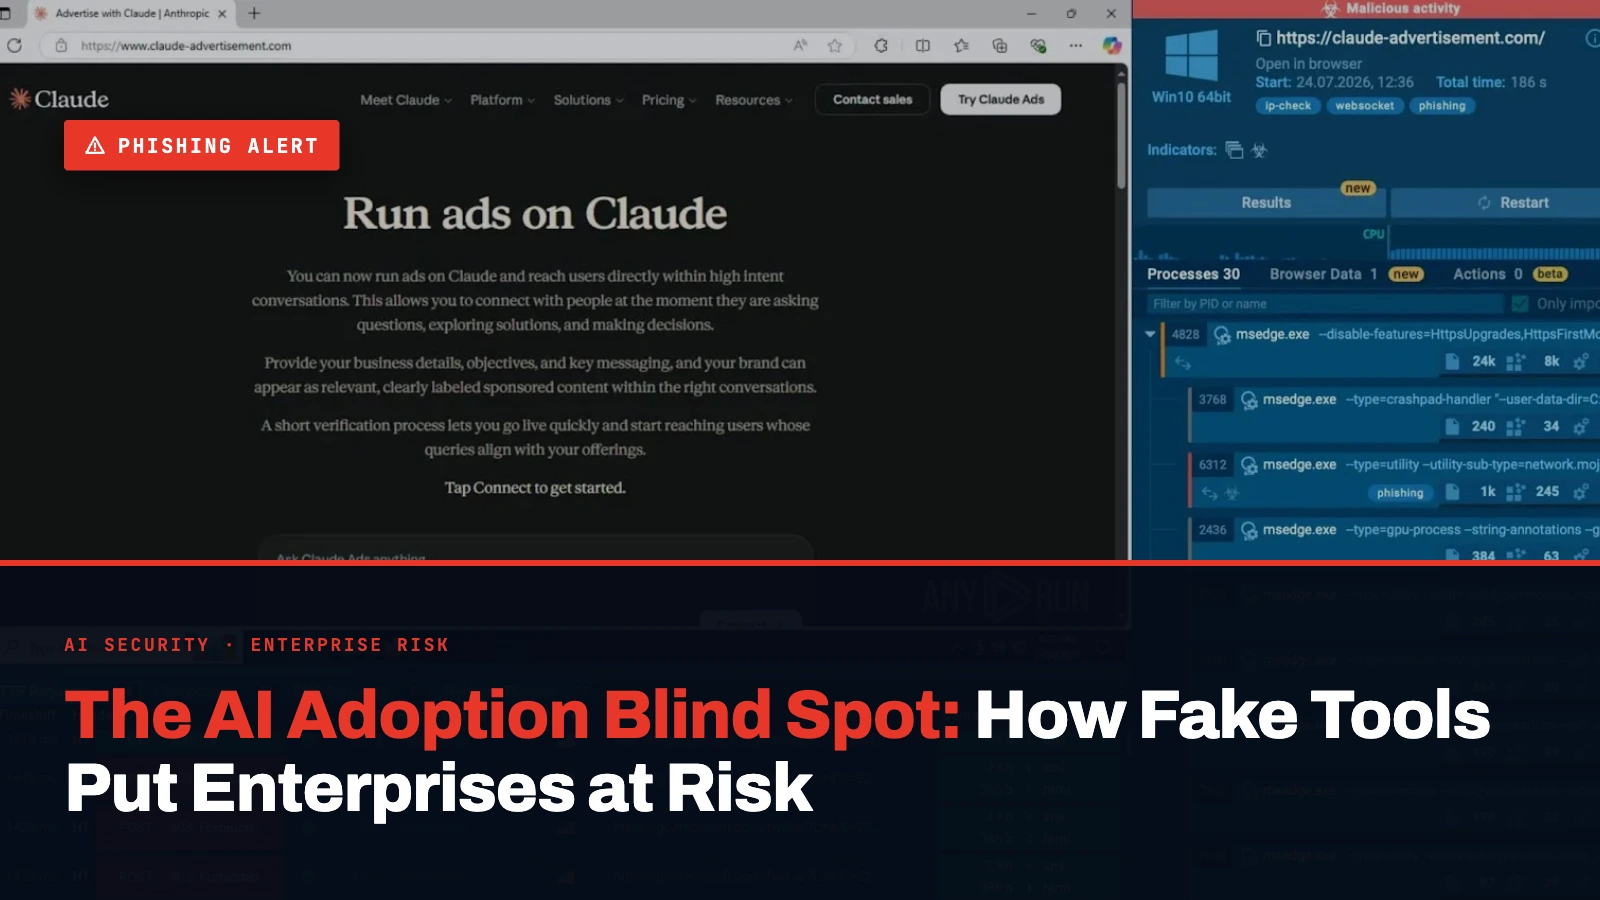
Attackers are also smart about tailoring their methods to specific employee roles. They know that a developer does not respond to the same tricks as a marketing manager, and a finance officer does not fall for the same lures as a customer support agent. So they customize each fake AI campaign around the tools and responsibilities of the people they are trying to deceive. Developers, for example, are unusually dependent on command-line interfaces, code assistants, and installation scripts. In one sandbox session observed by ANY.RUN researchers, a counterfeit GitHub Copilot CLI page delivered malicious installation instructions. The victim thought they were setting up a legitimate coding assistant. Instead, they were about to expose source code, cloud credentials, and API keys—the digital keys to an organization’s most valuable assets. Marketing teams face a different kind of risk. They often have access to advertising budgets, billing systems, and business accounts that can be abused for financial gain. A fake Claude Ads campaign used a fraudulent Google sign-in window to capture credentials, playing on the trust that marketing professionals place in familiar login pages. One wrong entry, and attackers gain access to advertising spend, campaign data, and connected business accounts. And then there are the broader groups of corporate users who simply want to install a desktop application. In one particularly clever attack, a trojanized Claude installer launched the legitimate application while quietly collecting browser data in the background. The employee saw the real Claude open on their screen and assumed everything was fine. Behind the scenes, their browser cookies, saved passwords, and session tokens were being harvested. This role-based approach reveals a deeper truth: fake AI threats are not limited to technology companies or IT departments. Exposure can arise anywhere employees install AI applications or connect business accounts without adequate security oversight. Every department, every team, and every role has its own vulnerabilities, and attackers are learning exactly how to press those buttons.
Understanding how these attacks unfold is essential for anyone responsible for protecting a business. Every fake AI campaign follows a surprisingly consistent chain, and at each step the employee plays a key role—sometimes without ever realizing it. The first stage is the initial lure. Attackers impersonate ChatGPT, Claude, Microsoft Copilot, or Google Gemini through counterfeit websites, paid advertisements, and even shared AI conversations. These lures are designed to look authentic, often appearing in search results right alongside legitimate links. The second stage is malicious delivery. Once the victim clicks a link, they are presented with fake installers or setup instructions. Instead of downloading a real program, they are tricked into downloading malware or executing malicious commands that are disguised as routine installation steps. The third stage is payload execution. Once launched, the malicious code deploys information stealers or other malware on the employee’s device. This is the moment when things go from bad to worse, because the attacker now has a foothold in the system. The fourth stage is credential theft. Attackers attempt to collect passwords, session cookies, authentication tokens, and any other sensitive data they can find. They are not just looking for one account; they are looking for every possible way into the corporate network. The final stage is business impact. With stolen credentials and compromised sessions, attackers can gain unauthorized access to corporate systems, potentially leading to data exposure, ransomware deployment, or further intrusion into connected platforms. What makes this chain particularly difficult to stop is that the employee performs the key step at every stage. They are not being tricked into ignoring warnings; they are being guided through a process that feels completely normal. By the time the malware runs, the damage is already underway. For security teams, this means detection has to happen early and response has to be fast. Waiting for a threat to announce itself is no longer an option.
One of the most important lessons from the research is that fake AI threats do not stop at Windows. Windows remains a major target for malware campaigns, and it will likely stay that way for years to come. But macOS devices are increasingly in the crosshairs too, and that creates new challenges for security operations. Fake AI installation pages can trick Mac users into copying malicious commands into Terminal, presenting dangerous actions as routine software setup instructions. A developer or a creative professional on a Mac might see a webpage that says, “To install Claude, open Terminal and paste this command.” That instruction looks official, and the user follows it without hesitation. In reality, they have just handed control of their system to an attacker. For enterprises with mixed operating systems, this creates an additional investigation challenge. Many security teams have limited visibility into macOS activity, which means they may not have the evidence needed to assess an incident. This can delay containment, leave affected accounts or devices unidentified, and allow attackers to move freely through the network. The solution is not to ignore Macs or assume they are safe. It is to ensure that security tools can analyze behavior across platforms consistently. Cross-platform behavioral analysis helps close this visibility gap. ANY.RUN’s Interactive Sandbox, for example, supports Windows, Linux, Android, and macOS, allowing analysts to investigate suspicious files and URLs in isolated environments. They can observe malicious behavior as it happens, examine network connections, extract indicators of compromise, and trace the full attack chain. This kind of investigation capability is no longer a luxury; it is a necessity in an environment where employees use a wide variety of devices and where attackers are constantly adapting their methods to exploit every platform. Without consistent visibility, SOC teams are left with blind spots, fragmented investigations, and no clear way to answer basic questions about what happened and what needs to be contained.
Closing the AI security visibility gap requires more than just adding another security tool. It requires a fundamental shift in how enterprises think about threat investigation. As AI adoption continues to grow, security teams need to be able to investigate threats disguised as legitimate applications before those threats turn into major incidents. This means looking beyond suspicious downloads to understand what actually executes on employee devices, which credentials may have been exposed, and whether an attack has progressed further into the corporate environment. It means giving analysts the ability to see, in real time, what a malicious file does when it runs, how it communicates, and what it leaves behind. When security teams have this level of visibility, they can make better decisions faster. The benefits are not just theoretical. More than 16,000 organizations worldwide use ANY.RUN to investigate cyber threats and strengthen their security operations. Teams using the solution report up to 36% higher detection rates, 21 minutes less time to respond to each incident, and 30% fewer Tier 1-to-Tier 2 escalations. For a busy security team, those improvements mean a lighter workload, faster containment, and more time to focus on the threats that actually matter. They also mean fewer unnecessary escalations, which allows senior analysts to concentrate on critical issues rather than drowning in routine alerts. As attackers continue to exploit trusted AI brands, the priority for security leaders is clear: give SOC teams the cross-platform visibility and behavioral evidence they need to identify malicious activity early and contain threats before they cause wider business disruption. The goal is not to scare employees away from using AI. AI is here to stay, and it offers enormous benefits. The goal is to make sure that when employees reach for the tools they trust, they are not unknowingly opening the door to attackers. With the right visibility, the right analysis tools, and the right mindset, security teams can stop more threats with the same team—and keep the promise of AI from turning into a corporate nightmare.