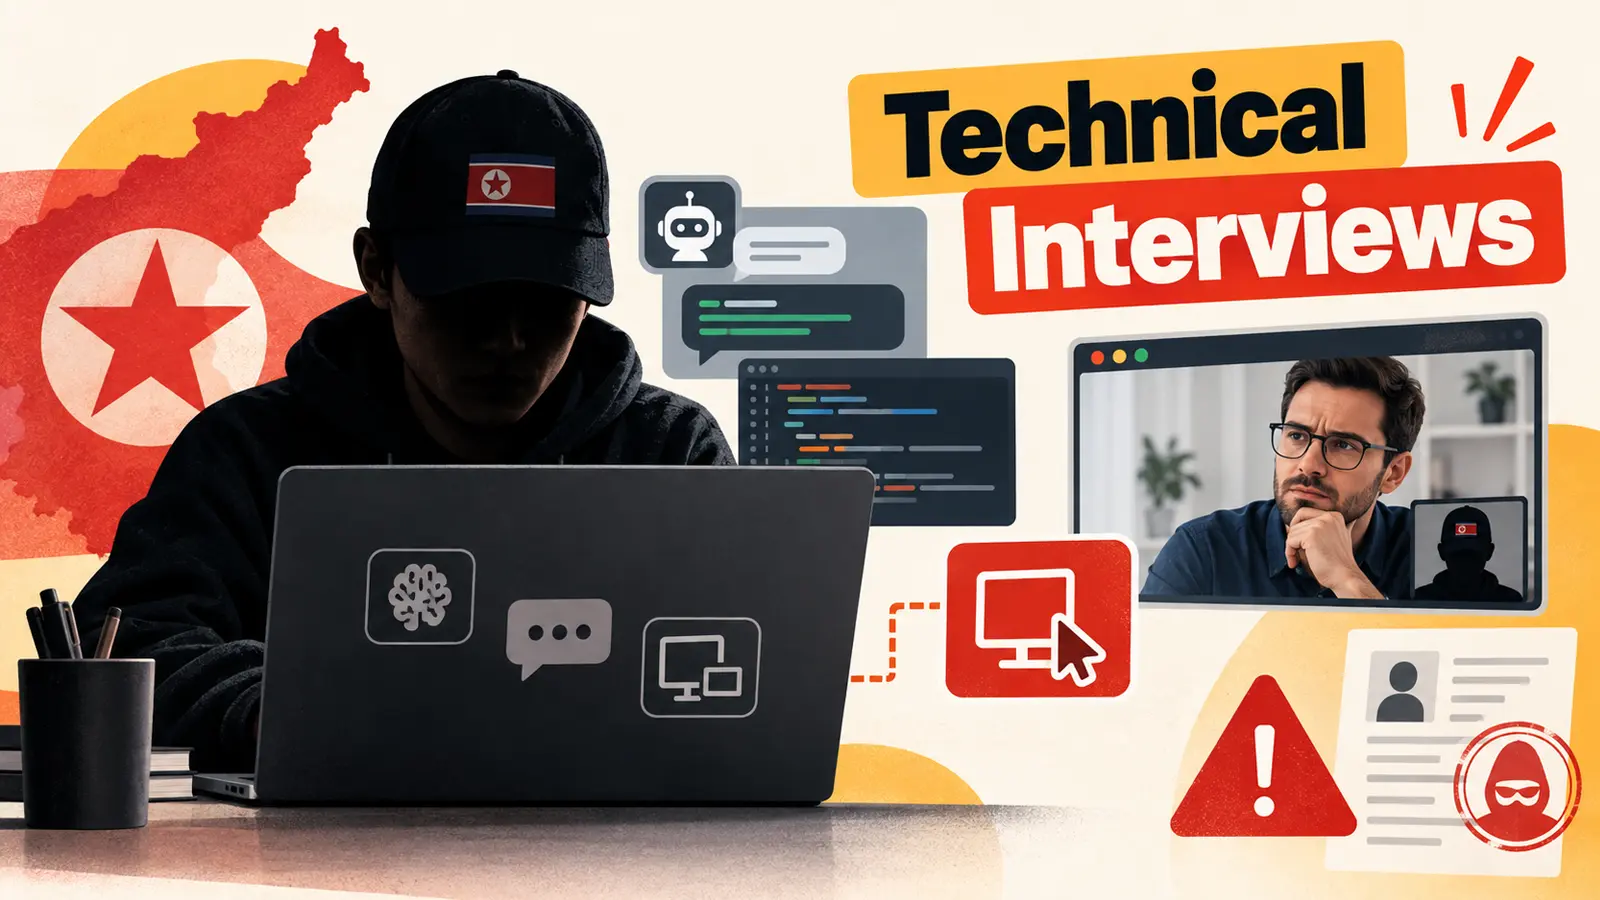
Imagine you are hiring for a remote position. The candidate on your screen has a polished resume, gives confident answers, and smiles at the right moments. It feels like a normal interview. But the person you are talking to may not be the person who will actually do the work. According to a report from Silent Push, shared by Cyber Security News, North Korean operators are using a disturbing mix of artificial intelligence, remote-control software, and hired stand-ins to make fraudulent job candidates look completely genuine during technical interviews. This is not a traditional malware campaign, but it is just as dangerous. It turns a routine hiring process into a gateway for sanctions evasion, payroll fraud, data theft, and unauthorized access to company systems. The scheme was uncovered after a suspicious job advertisement appeared in the Mouse Review Discord community. That ad sought people in the United States, Europe, and Latin America who would appear on camera, communicate with employers, and lend their local identities to a hidden remote worker operating behind the scenes. In other words, they were looking for human masks.
The job advertisement described the proxy arrangement in surprisingly direct terms. A local participant would turn on a camera, speak with clients, and present the required skills, while the real operator supplied help in real time. The pitch offered the proxy 35 percent of the money and kept 65 percent for the hidden worker. That kind of split is not a typical freelance arrangement; it is a partnership designed to deceive an employer. Silent Push researchers engaged the person behind the ad using a controlled persona, and they assessed with moderate to high confidence that the representative, known as Tec Guru, was a North Korean IT worker. That assessment was based on technical references, operational details, and observed language patterns. The investigation revealed that this is not merely a strange corner of the gig economy. It is a serious entry point for later abuse. A company can unknowingly hire someone whose interview performance, identity, location, and actual work are all supplied by different people. Once hired, that phantom employee may be granted access to sensitive systems, proprietary code, and internal communications. In a related case involving AI resume identity fraud, a suspected operative allegedly used forged career material and a VoIP number to pursue a remote position, showing that this kind of deception is spreading beyond a single isolated incident.
The technical toolbox behind these fake candidates is surprisingly ordinary, which makes the scheme even harder to detect. Tec Guru offered live coaching through Google Meet, meaning the visible candidate could receive real-time prompts on what to say and how to act. The operator also proposed using AI tools like ChatGPT to fill knowledge gaps while the proxy remained on screen. During coding exercises, the plan involved remote access software, allowing another person to complete the technical work while the visible candidate kept the conversation moving and appeared to be the one solving problems. Tools such as AnyDesk, TeamViewer, and Chrome Remote Desktop make that handoff extremely easy, especially when an interviewer is focused only on a shared screen and does not realize that someone else is typing. The same concern appeared in other reporting on forged IDs and remote desktops, where remote-management software was linked to efforts to hide the real worker’s activity. The representative also advised the researchers to use Astrill VPN. Along with Telegram and a US-style VoIP number, that recommendation was part of the operational picture. None of these tools alone proves wrongdoing, but together they paint a clear picture of a carefully constructed deception designed to hide identity, location, and true intent.
The immediate danger is not limited to a weak interview. Once a fraudulent worker is hired, the organization may face a far more serious threat: an insider who can copy proprietary code, collect sensitive information, or demand money in exchange for not publishing stolen material. The financial risks are also significant. Payments can be routed through a proxy’s bank account before funds are transferred onward, making it difficult to trace where the money actually goes. Companies may also face sanctions exposure if they unknowingly pay a North Korean worker through an intermediary. A multinational warning issued on July 31, 2026 urged organizations to strengthen identity checks and scrutinize payment anomalies, reflecting a growing concern that is also covered in warnings about North Korean workers infiltrating companies through fake employment. This is not just a problem for large tech companies. Any organization that hires remote workers, especially for roles involving access to data, code, or financial systems, could be caught in this trap. The attackers are not breaking down firewalls; they are walking through the front door by exploiting trust, human nature, and the gaps between HR, security, and finance.
Hiring teams need to treat this risk seriously and update their controls accordingly. They should verify a candidate’s physical location using independent checks, rather than simply trusting whatever the candidate says or relying on a video call. Identification documents and payment details should be carefully matched, and any unusual account changes should be treated as warning signs. Live interviews should include managed video verification and technical exercises that can detect outside assistance, rather than relying on a single camera feed. Companies should also limit new hires to only the access they need for their role, monitor early account activity for anomalies, and investigate unexpected remote-control tools or prolonged sessions. These precautions matter because fake-worker operations can overlap with recruiter-led attacks, including North Korean worker campaigns that use malicious coding tasks against job seekers. The investigation shows how easily a fraud operation can blend social engineering with common workplace technology. No single control will catch every attacker, but a layered approach can make it much harder for someone to hide behind a fake identity. Organizations should treat recruitment as part of their security perimeter: verify the person, verify the location, and make sure that the person completing the interview is the one who will receive access after hiring.
For those investigating similar threats, Silent Push shared specific indicators of compromise. The Discord account used to post the fraudulent recruitment advertisement was tecguru113, with the account ID 1453753519436861505. The Telegram handle used by the representative during the investigation was @tecguru0618. IP addresses and domains were intentionally defanged to prevent accidental resolution or hyperlinking, and re-fanging should only be done within controlled threat intelligence platforms. These indicators can help security teams identify related activity and connect seemingly unrelated incidents. But the lesson goes beyond a single account or handle. The most advanced security tools cannot protect an organization if the front door is open to an impostor. This scheme exploits human trust, not technical vulnerabilities, and that makes it especially dangerous. Every hiring manager, recruiter, and security professional should understand that the person on the screen is not necessarily the person behind the keyboard. The story of Tec Guru is a reminder that in a world of remote work, digital identities, and AI-assisted communication, the human element is part of the security perimeter. Awareness, verification, and healthy skepticism are no longer optional. They are the first line of defense against a quiet, patient, and highly organized form of fraud that turns ordinary job interviews into a serious national security and corporate risk.