If you’ve ever been online for more than a few hours, you’ve probably seen the fake warnings: a sudden full-screen popup that resembles an antivirus scan, complete with scary red numbers and a button that says “Fix now.” Or an urgent message claiming your browser is out of date and you need to download the latest update immediately. These aren’t isolated glitches. They’re part of a vast scam economy that has learned to impersonate trusted brands, browser interfaces, and system alerts to trick ordinary people into installing malware, handing over passwords, or granting remote access to their computers. As these attacks have become more convincing, the line between a real warning and a fraudulent one has blurred. That’s why Google’s recent decision to upgrade Chrome’s Enhanced Protection mode is such an important step. On October 20, 2026, the company announced that Chrome will now use a more powerful Gemini AI model to spot fake antivirus alerts, fraudulent browser update scams, and other deceptive websites in real time. The move is more than a routine security update; it represents a fundamental shift in how a browser can defend people against scams that are designed to mimic the browser itself. Instead of relying solely on blocklists and old-school pattern matching, Chrome is beginning to reason about what a page is trying to do—and whether that intent is malicious.
The upgrade also marks a technical turning point. Earlier versions of Chrome’s AI scam detection relied on a compact Gemini model that ran directly on your device. That approach had real privacy advantages, but it came with a significant limitation: not every computer or phone has the hardware muscle to run a sophisticated language model locally. In practice, that meant AI-powered scam detection was available only to people with relatively modern, high-powered devices. Everyone else remained on the older, less adaptive protections. With this latest update, Google has moved the analysis to a server-side model, meaning the heavy lifting happens in Google’s cloud rather than on your laptop or phone. That may sound like a small engineering detail, but it changes the stakes. It allows Google to use a much larger, more robust Gemini model—the kind that can parse subtle language cues, detect emotional manipulation, and understand the context of a webpage far better than a portable version could. More importantly, it makes these protections available to all users who switch on Enhanced Protection, regardless of the hardware they’re using. The catch, of course, is that sending page content to Google’s servers raises familiar privacy questions. Google has tried to address those concerns by stating that page text is sent for analysis only when a website shows strong scam indicators. The company also says that this content is processed temporarily and is never logged, retained, or used for training its models. For many users, that will be a reassuring compromise: privacy safeguards remain in place, but the intelligence powering the protection is no longer held back by the limits of a phone’s processor.
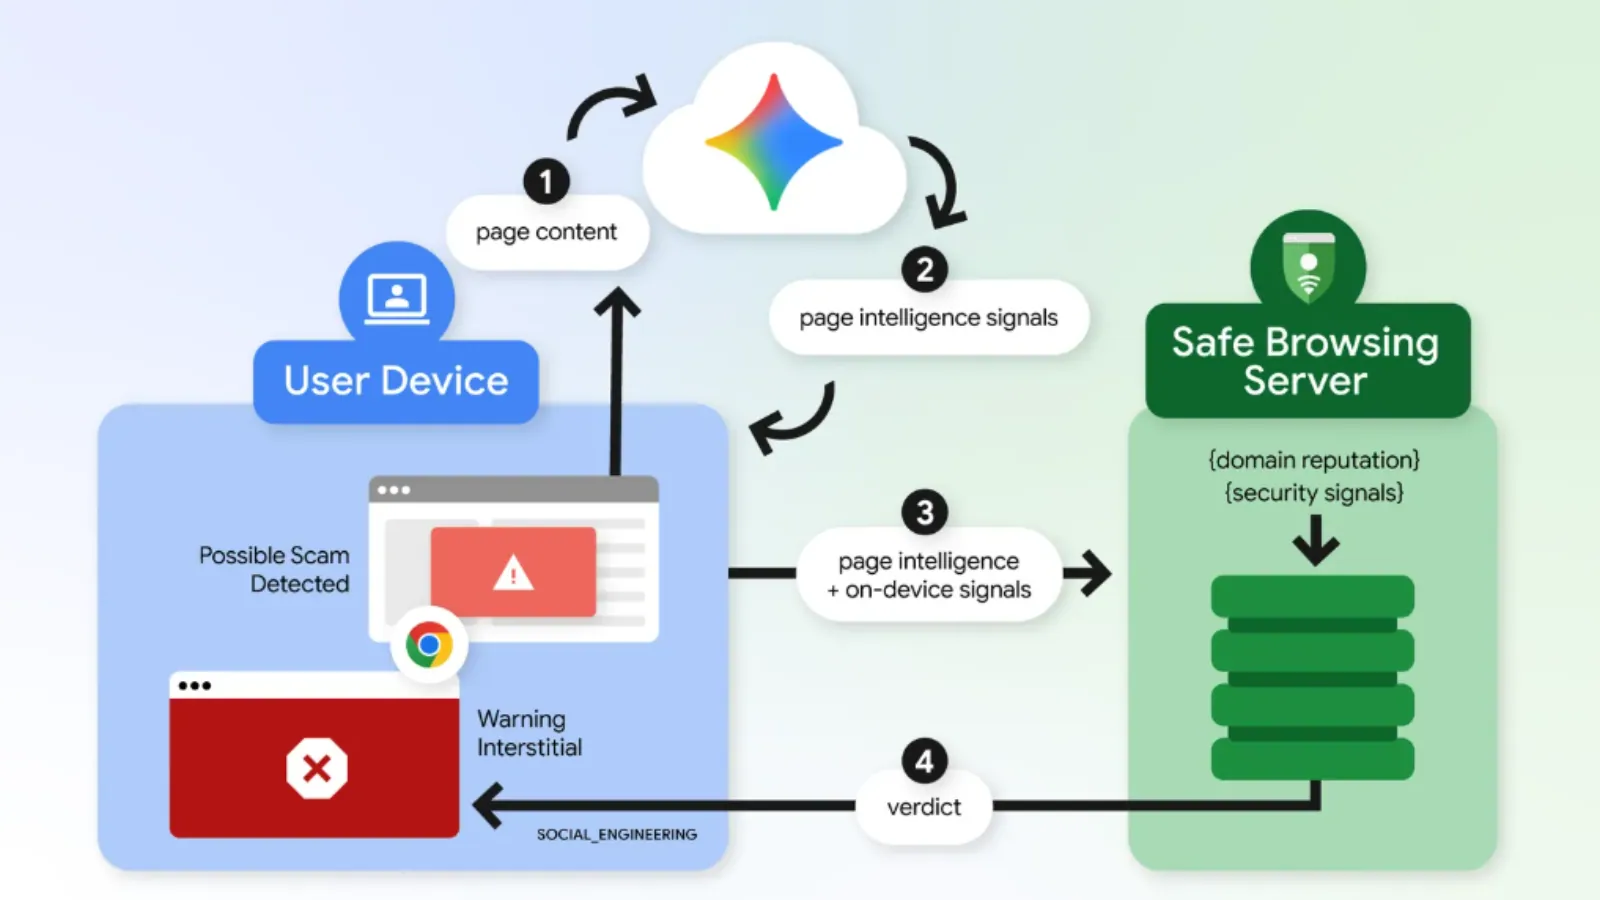
Understanding how the new system works helps make sense of why it’s such a leap forward. When you visit a page that triggers possible scam signals, Gemini examines the content itself, looking for signs of fraud. It’s not just scanning for keywords like “virus” or “security alert.” The model attempts to identify the brand the website claims to represent—perhaps Microsoft, Apple, or Norton—and then assesses the page’s intended purpose. Is it trying to provide information, ask you to sign in, or pressure you into calling a phone number? From that analysis, Gemini produces a score indicating how likely it is that the page is a scam. But here’s an important detail: Gemini does not make the final decision on its own. Safe Browsing combines the Gemini assessment with other signals, including domain reputation, historical data, and known malicious infrastructure. This layered approach means a weirdly worded page isn’t blocked just because it sounds suspicious; it has to fit a broader picture of a scam. If a domain has a good reputation and no history of abuse, a single odd phrase won’t trigger a warning. Conversely, if a brand-new domain is already associated with suspicious behavior and the Gemini model detects a familiar scam narrative, the combined evidence can lead to a warning. This two-step verification is crucial, because it reduces the risk of false positives. It also means the AI is not acting as an unchecked judge; it’s another witness whose testimony is weighed alongside other evidence.
One of the most visible changes is how Chrome communicates danger to you. Previously, the browser essentially had one dramatic response for malicious sites: a full-page red warning that effectively said “Get out.” That approach is fine when a site is clearly dangerous, but it creates a dilemma for genuinely suspicious pages that don’t yet meet the threshold for “confirmed dangerous.” If Chrome ignored those pages, users stayed vulnerable; if it showed the same red screen, it risked crying wolf. Google’s answer in this update is a two-tiered warning system. Enhanced Protection users will now see “suspicious site warnings” for pages that exhibit deceptive patterns but haven’t been confirmed as malicious. These warnings are intentionally different in appearance, wording, colors, and icons from the full-page red warnings used for known dangerous websites. The design distinction isn’t arbitrary; it’s a deliberate psychological and practical strategy. When you see a red page, you know Chrome is highly confident that the site is dangerous. When you see a more subdued suspicious-site warning, you’re being told to slow down and think, but the browser hasn’t slammed the brakes. This nuance helps preserve the impact of the most serious warnings while allowing Chrome to flag a broader range of potentially harmful pages. It also acknowledges that the internet is full of gray areas—pages that aren’t quite malicious enough to be blocked outright but are still deliberately deceptive. The new system gives users more information without overwhelming them with false alarms. Google hopes this will reduce warning fatigue, the tendency people develop to ignore security messages when they see too many of them.
The update also takes direct aim at one of the most troublesome attack techniques to emerge in recent years: ClickFix. You’ve likely encountered the pattern without realizing it. A webpage displays a fake error message—maybe it says your browser isn’t working properly, or a video won’t play, or your system has a critical virus. The page then instructs you to click a button, copy a command, and paste it into a program like PowerShell or the Windows Command Prompt. The pretense is that you’re “fixing” the problem. In reality, you’re executing the attacker’s code. Because the malware is launched through your system’s own command-line tools, it bypasses Chrome’s normal download protections entirely. There’s no file to scan, no download warning, just a clipboard and a terminal window doing the dirty work. Google’s earlier reporting on fake Chrome error pages and fake browser updates, such as the DriveSurge campaign, showed how attackers combine familiar update prompts with command-based infection methods. The new Chrome defenses are designed to interrupt this process. If you copy a suspicious command during a potential ClickFix attempt, Chrome can detect what’s happening, strip out any personally identifiable information from the copied content, and send the relevant details to Safe Browsing for analysis. If the verdict is dangerous, you’ll see a warning. Google says it has also built in checks to avoid disrupting legitimate developer work—after all, plenty of real troubleshooting instructions rely on copy-paste commands. The challenge is distinguishing between a developer setting up a dev environment and a grandma being tricked into running a PowerShell script. The new system tries to make that distinction by looking at the context and the command itself, not just the act of copying text. It’s a delicate balance, but one that’s essential for stopping this increasingly common vector.
For all this to work, you have to take one important step: enabling Enhanced Protection in Chrome’s Safe Browsing settings. It’s not on by default, and features like the new suspicious-site warnings and ClickFix detection are only available to users who turn it on. Google provides clear instructions in its Chrome Safe Browsing guide, and the company stresses that Chrome will never ask you to repair the browser by copying and running commands from a webpage. If you see such a request, it’s a scam. The bigger takeaway, though, is that browser security is evolving from a simple filter into an intelligent interpreter of human intent. Google’s use of Gemini in this context is a recognition that modern scams don’t always look like malware; they look like communication. They use persuasion, urgency, and imitation. Fighting them effectively requires a tool that can understand language and context, not just a static list of bad URLs. There are, of course, limits to any AI-based protection. Scammers will adapt, find new loopholes, and test the edges of the model. But the shift to a server-side Gemini model gives defenders a significant edge: the ability to update and improve the model continuously, without waiting for users to install a browser update. It also levels the playing field, bringing high-end AI protection to everyone, not just people with the newest hardware. Ultimately, this is a reminder that security is a shared responsibility. Chrome’s enhanced warnings are powerful tools, but they work best when paired with a healthy dose of human caution. If a website demands that you copy a command into a terminal, or if an alarming alert appears out of nowhere, pause. A real security warning from Chrome will never ask you to run code, call a “support center,” or install a fresh “update” from a website. The new AI is a strong ally, but you’re still the strongest line of defense.