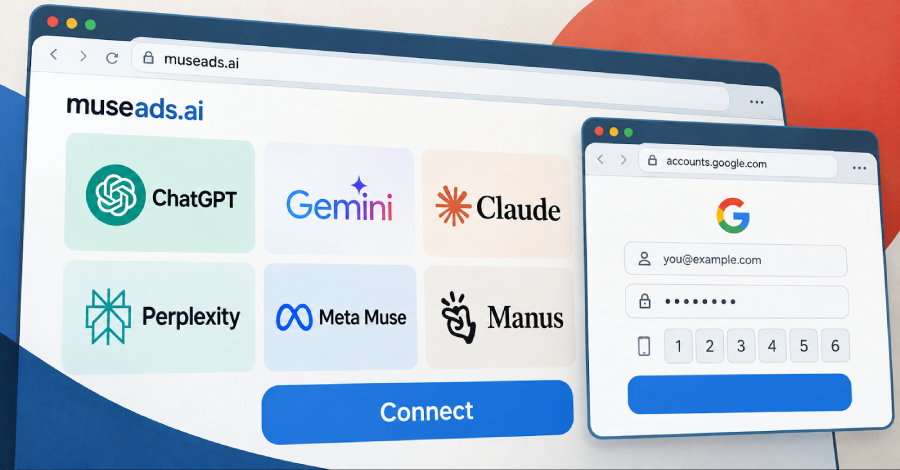
Picture this: you’re a media buyer or an agency marketer, and you get an email that looks like it came from a trusted name in tech. It’s promoting a sleek new advertising tool for one of the big AI chatbots—maybe Google Gemini, OpenAI’s ChatGPT, Anthropic’s Claude, Perplexity, Meta’s Muse, or even the newer Manus. The landing page looks polished. It promises campaign optimization, spend audits, and easy connections to your business ad accounts. There’s a button that says “Connect.” It seems completely normal. But it’s all a carefully built trap. Cybersecurity researchers at Island have uncovered what they describe as a “human-operated phishing platform” that impersonates these AI advertising products for one reason: to steal your login credentials and your multi-factor authentication codes. The attackers aren’t using some crude fake login page that you could spot from a mile away. Instead, they use a technique called browser-in-the-browser, or BitB, to create a fake browser window inside your real browser. That fake window looks so authentic that even experienced users can be fooled. The entire operation is designed to make you believe you’re signing into your Google, Meta, TikTok, or Okta account when you’re actually handing your secrets directly to a criminal.
The technical details are both fascinating and frightening. Every one of these fake products is built around the same action: Connect. When a visitor clicks that button, the phishing platform draws a browser window right inside the actual browser. The fake address bar displays trusted origins like accounts.google.com or a legitimate Okta tenant, so your eye tells you this is a real sign-in page. But the real browser never leaves the phishing domain. Behind the interface, the platform is doing much more than just collecting passwords. It records every password attempt, fingerprints the device by gathering information about your browser, operating system, screen resolution, and other identifying details, and then sends that data to the attacker through a real-time communication channel called Socket.IO. The attacker, sitting at a control panel, can see what the victim is typing and doing in real time. They can then decide which MFA challenge to show next. This isn’t an automated credential harvester; it’s a live, human-driven operation. The attacker can request another password, show an SMS or authenticator code prompt, display a Google approval prompt, ask for a QR code scan, or even present number-matching screens from Okta. They can reject a submitted code with a “wrong code” message to keep the victim trying, or they can end the conversation entirely. Commands flow through events called operator-command and telegram-command, and both are fed into the same parser, meaning the attacker can steer the victim through every step of authentication as if they were sitting right next to them.
What makes this campaign especially clever is how each fake product is tailored to its audience. The researchers noted that every brand gets its own pitch. ChatGPT promises a Monday Google Ads brief. Gemini promises support for manager accounts and linked clients. Claude gets its own advertising portal. Perplexity offers campaign planning and spend audits. Manus offers a private Meta integration. One of the websites, museads.ai, appeared on September 16, 2026, just over a week after Meta launched its Muse AI agent. The site described itself as “Your AI ads manager for paid media workflows” and claimed to help customers reach buyers, connect ad accounts, and run sponsored placements. On the spoofed page, a Prompt Box with a Connect button triggers the BitB attack. The attackers are clearly paying attention to the news cycle, launching lookalike products that feel timely and relevant. They also use fake invitation emails that impersonate these trusted brands, giving the whole scheme a veneer of legitimacy. If you’re a busy marketer who just heard about a new AI tool from a trusted company, an email inviting you to try it doesn’t seem suspicious. You click, you connect, and you’ve just given away access to your advertising accounts. The researchers emphasized that these pages move with the news, which is why they can be so effective.
This AI ads campaign is not an isolated incident. Island says it’s part of a broader phishing platform that supports a three-pronged operation. Alongside the fake AI advertising tools, the same attackers run Google Ads-themed refund claims and payment confirmation pages, as well as recruitment-related sites for well-known companies like Tesla, Louis Vuitton, Nike, and Adecco. All of these websites share the same underlying technology stack, built with Next.js and Socket.IO, and they communicate with the same endpoints. That tells researchers they’re all part of one unified infrastructure, even if the outward appearance changes from one scam to another. In a surprising twist, the threat actors behind the operation have also exposed source code for earlier versions of their platform through misconfigured public GitHub repositories. That means security researchers can study exactly how the phishing platform works, and it also shows that the attackers are constantly iterating and improving their tools. The shared infrastructure and exposed code give defenders a rare glimpse into the inner workings of a professional, human-operated phishing operation. It’s not a random teenager in a basement; this is a well-organized criminal enterprise with a clear playbook and the technical skill to build convincing fake products at scale.
The people behind this campaign are going after a very specific group: agency staff, media buyers, and manager-account administrators. That makes sense because these are the people who have access to high-value advertising accounts. The attackers’ likely goal is to monetize those accounts by running their own ad campaigns or selling them for profit, especially if the accounts have a clean spending history. A report from Mimecast published in July 2026 highlighted how malware families like VietCredCare, DuckTail, NodeStealer, and PXA Stealer have already made ad account theft a widespread commodity crime. Bad actors drain business budgets and sell accounts with good reputations in underground markets. For the victim, the impact can be devastating. The credit card on file is the easy part; you can cancel it within hours. Getting the account back is another story. Attackers typically add their own administrators and downgrade the legitimate owner, so the original user loses access. Recovery can take weeks or months, and during that time the account keeps serving ads, spending money, and potentially damaging the brand’s reputation. For a manager account, the damage doesn’t stop with one business. It reaches every client connected to that agency, multiplying the harm and making the incident much more than a simple account takeover.
So what can organizations do to protect themselves? Island recommends enabling phishing-resistant authentication wherever possible, because even a well-crafted BitB attack struggles to bypass hardware security keys or other phishing-resistant methods. Organizations should also review advertising control changes carefully and scrutinize any AI integration before connecting it to business accounts. If an invitation or a product seems too good to be true, it probably is. The disclosure also comes alongside another disturbing finding from Island: threat actors are abusing Google-sponsored results to route unsuspecting users to custom GPTs or shared-AI chat content. Those pages then redirect users to a fake Cloudflare verification page that serves ClickFix-style lures, tricking people into copying and pasting malicious commands that deliver a remote access trojan called NetSupport RAT. This campaign didn’t require any vulnerability in ChatGPT or Google. It simply abused trusted platforms, attacker-authored content, paid search, and social engineering to move people toward malware delivery. Over a three-month observation period ending in August 2026, the broader delivery cluster included about 850 paid-ad landings, 26 lookalike ChatGPT destinations, and 71 Google Ads campaign IDs. The takeaway is clear: in a world where AI tools are becoming essential to daily work, attackers are following right behind, building convincing fakes and using every trick in the book to steal credentials, hijack accounts, and drain budgets. The best defense is a healthy dose of skepticism, strong authentication, and a careful review of every connection you make.