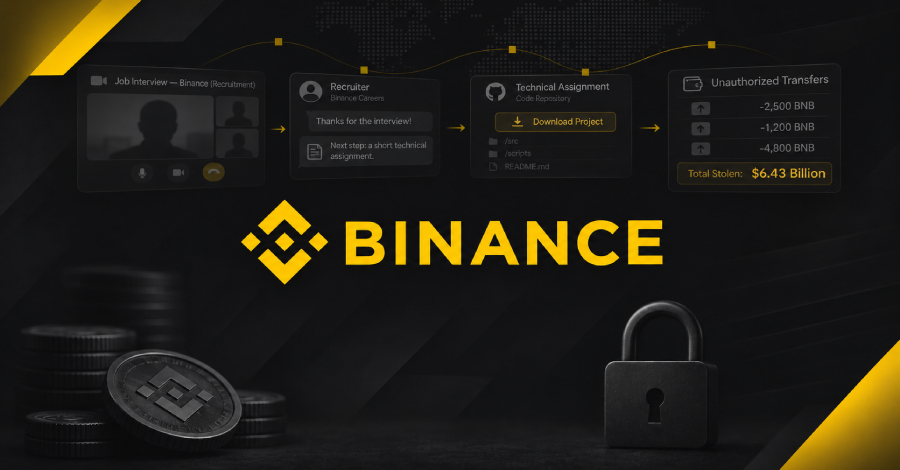
When most people picture a cryptocurrency heist, they imagine a hooded figure cracking codes or a virus silently draining a digital wallet. But the theft of $6.43 billion from Binance, the world’s largest cryptocurrency exchange, was something far more complex and unsettling. Binance has described it as the final act of a “sophisticated, multi-stage campaign” that unfolded over months and combined many different kinds of attack: fake job interviews, malicious software disguised as developer tools, a compromised internal AI system, hijacked endpoints, and a method of tricking the exchange’s own transaction-authorization process. The company was clear that this was not a single isolated breach or a simple phishing incident. It was a coordinated operation that used social engineering to target specific people, then leveraged those personal footholds to move deeper into Binance’s wallet infrastructure. The attackers did not just steal a password and run. They studied the company, identified the engineers who held access to critical systems, and built a chain of compromises that ultimately allowed them to authorize transactions outside the normal withdrawal process. In that sense, the heist was as much a psychological exploit as a technical one. Binance’s own account of the incident reads like a corporate espionage thriller: attackers who posed as recruiters, infected a developer’s computer through a poisoned open-source installer, turned an internal AI tool into a weapon, and covered their tracks so carefully that the breach was not fully understood until long after it had begun. The scale of the loss is almost numbing, but the story behind it is a reminder that even the most advanced security systems can be undone by human trust, curiosity, and the daily routines of ordinary employees. It also raises the uncomfortable possibility that the attackers knew exactly whom to target and when, and that every move was planned with the patience of a spy operation rather than the chaos of a typical cybercrime.
The first domino fell quietly, in June 2026, when an engineer in Binance’s Wallet DevOps team—referred to as Engineer A—went looking for a popular artificial intelligence tool online. Instead of landing on a legitimate source, the engineer encountered a search result that led to a trojanized Homebrew installer. Homebrew is a widely used package manager for macOS, and many developers trust it without a second thought. The poisoned installer contained malicious code, and when Engineer A ran it, the machine was compromised. This was a supply chain attack: the software itself looked normal, and the installation process seemed routine. Binance says it detected the intrusion and rotated all related credentials as a precaution. But the damage was not limited to the infected computer. The attackers had already learned something just as valuable: Engineer A’s role, and the identities and functions of his colleagues on the wallet infrastructure team. That information would become the key to everything that followed. In hindsight, the June incident was not the end of the attack but the beginning of a reconnaissance mission. The attackers did not try to steal funds immediately. They quietly gathered intelligence about how Binance’s wallet team was structured, who had access to what, and where the real security boundaries lay. It was a slow, methodical process, and it shows how dangerous a single compromised developer machine can be when the attacker is patient enough to map the entire terrain before striking. For Engineer A, the search for a convenient tool was an everyday act; for the attackers, it was the perfect entry point into a fortress that otherwise might have held firm.
The second stage was even more personal. In September 2026, another Binance engineer—Engineer B—was contacted on a legitimate job-hunting platform by someone pretending to be a Project Director. The fake director arranged a first-round interview with someone playing the role of an HR representative. The HR persona shared a social media account filled with personal photos and videos, all designed to make the fiction feel real. Then came a second interview with someone claiming to be the CEO of a nonexistent company. The interview itself took place on a popular social chat app, which made the whole process feel casual and modern. Near the end of the conversation, Engineer B was asked to download an “assignment”—a malicious code repository—onto his work computer. This was the trap. The repository contained code that executed during the setup process and began a series of unauthorized activities without raising any obvious alarms. Binance described the malware as highly advanced, using obfuscation and evasion techniques to hide its presence. At some point, the malware swapped out a legitimate development tool component for a poisoned version, allowing it to execute commands and communicate with a server controlled by the attackers. It also took steps to erase forensic artifacts, making it harder for investigators to see what had happened. For Engineer B, this may have felt like a normal job interview, a moment of professional opportunity. In reality, it was a carefully staged performance designed to exploit the natural excitement and trust that come with a promising career move. The attackers understood that engineers are used to downloading code and trying things out; they simply turned that professional habit into a weapon. The use of a real job platform, the creation of a believable persona, and the gradual escalation of trust over multiple conversations made the trap almost impossible to spot until it was far too late.
By October 20, the attackers had everything they needed to move laterally. Using Engineer B’s compromised computer, they abused an internal AI tool to gain control over Engineer A and another employee, Software Engineer C. This is a particularly chilling detail: the same AI systems Binance had built to help its engineers were now being used to manipulate access and extend the attackers’ reach. The intruders soon discovered that Engineer A had a container deployment permission token on his computer—a powerful credential that allowed the deployment of containers in Binance’s environment. Then, on October 29, between 17:15 and 19:56, the attacker logged into Software Engineer C’s computer, used the credentials stolen from Engineer A, deployed a container, and triggered a malicious script to launch the attack. The unauthorized access ultimately allowed the attacker to reach an internal wallet signing service and initiate transactions that were not part of the normal withdrawal process. In other words, the attackers had assembled a chain of keys: Engineer B’s machine gave them entry, the internal AI tool gave them control, Engineer A’s token gave them power, and Engineer C’s computer gave them a place to stand. The result was the largest theft in the history of cryptocurrency. The precision of the timing—the entire attack sequence was carried out in under three hours—suggests that the attackers had rehearsed the final move carefully and were waiting for the right moment. They did not need to break encryption or exploit a bug in the blockchain. They simply needed to become trusted users inside the system, and that is exactly what they did.
Binance’s response to the catastrophe has been comprehensive, and the company has gone to unusual lengths to explain what went wrong. It has reconstructed the affected wallet system in a new environment, rebuilt the internal AI tool, and overhauled access controls. It replaced affected devices, decommissioned credentials and tokens belonging to the engineers involved, and completed enhanced security scans across all employee devices. It also strengthened wallet-service risk controls, expanded AI-based behavioral anomaly detection, and worked with law enforcement, blockchain intelligence firms, and industry partners to trace and freeze affected assets. Binance says the entry points used in the attack have been closed, and systems touched in the attack path have been rebuilt or replaced. The company is also investing more heavily in AI-enabled detection, endpoint protection, developer-environment security, and behavioral anomaly monitoring. The scale of the response reflects the scale of the breach. Recovering $6.43 billion is not a simple matter of reversing a transaction, especially when the attackers have had months to move funds and obscure their tracks. But Binance’s willingness to describe the attack in detail—including the human errors and technical failures—is a rare and valuable step. It also raises uncomfortable questions for the entire cryptocurrency industry. If Binance, with its massive security team and advanced tools, could be compromised in this way, what about smaller exchanges and platforms? The attack was not a one-off trick; it was a campaign that used familiar, everyday behaviors—searching for software, chatting with recruiters, downloading an assignment—to bypass some of the strongest defenses in the industry. The rebuilding process, Binance suggests, is not just about restoring services but about rethinking how security works from the ground up, with humans as the first line of defense and the first point of risk.
This attack did not happen in a vacuum. Binance says that since the start of the year, it has foiled 57 suspected cyber threats linked to North Korea, underscoring how persistent and aggressive the attacks on cryptocurrency companies have become. The techniques described in this incident fit a broader pattern: fraudulent job interviews, malicious software disguised as popular developer tools, compromised software packages and browser extensions, fake video conferencing applications, and social engineering campaigns designed to steal credentials or deploy remote access malware. These are not random opportunists. They are well-funded, patient, and highly organized groups that treat cryptocurrency exchanges as high-value targets. The use of fake recruitment interviews is especially notable because it preys on the way modern professionals work: people switch jobs, network online, and regularly download software to evaluate opportunities. In the Binance case, the attackers used a legitimate job platform and realistic personas to build trust over multiple conversations. By the time Engineer B was asked to download the assignment, the interaction felt normal. That is the terrifying power of social engineering—it turns human kindness, ambition, and curiosity into attack vectors. For the broader crypto industry, the lesson is clear: security cannot stop at code and firewalls. It must include rigorous verification of external communications, careful controls on developer environments, and a culture that encourages employees to question even the most plausible requests. Binance has promised to keep investing in detection and response, but no single company can eliminate the risk. The attackers will adapt, find new ways in, and continue to test the boundaries of trust. The $6.43 billion theft is a painful reminder that in the world of digital assets, the weakest link is often not the encryption—it is the person at the keyboard.