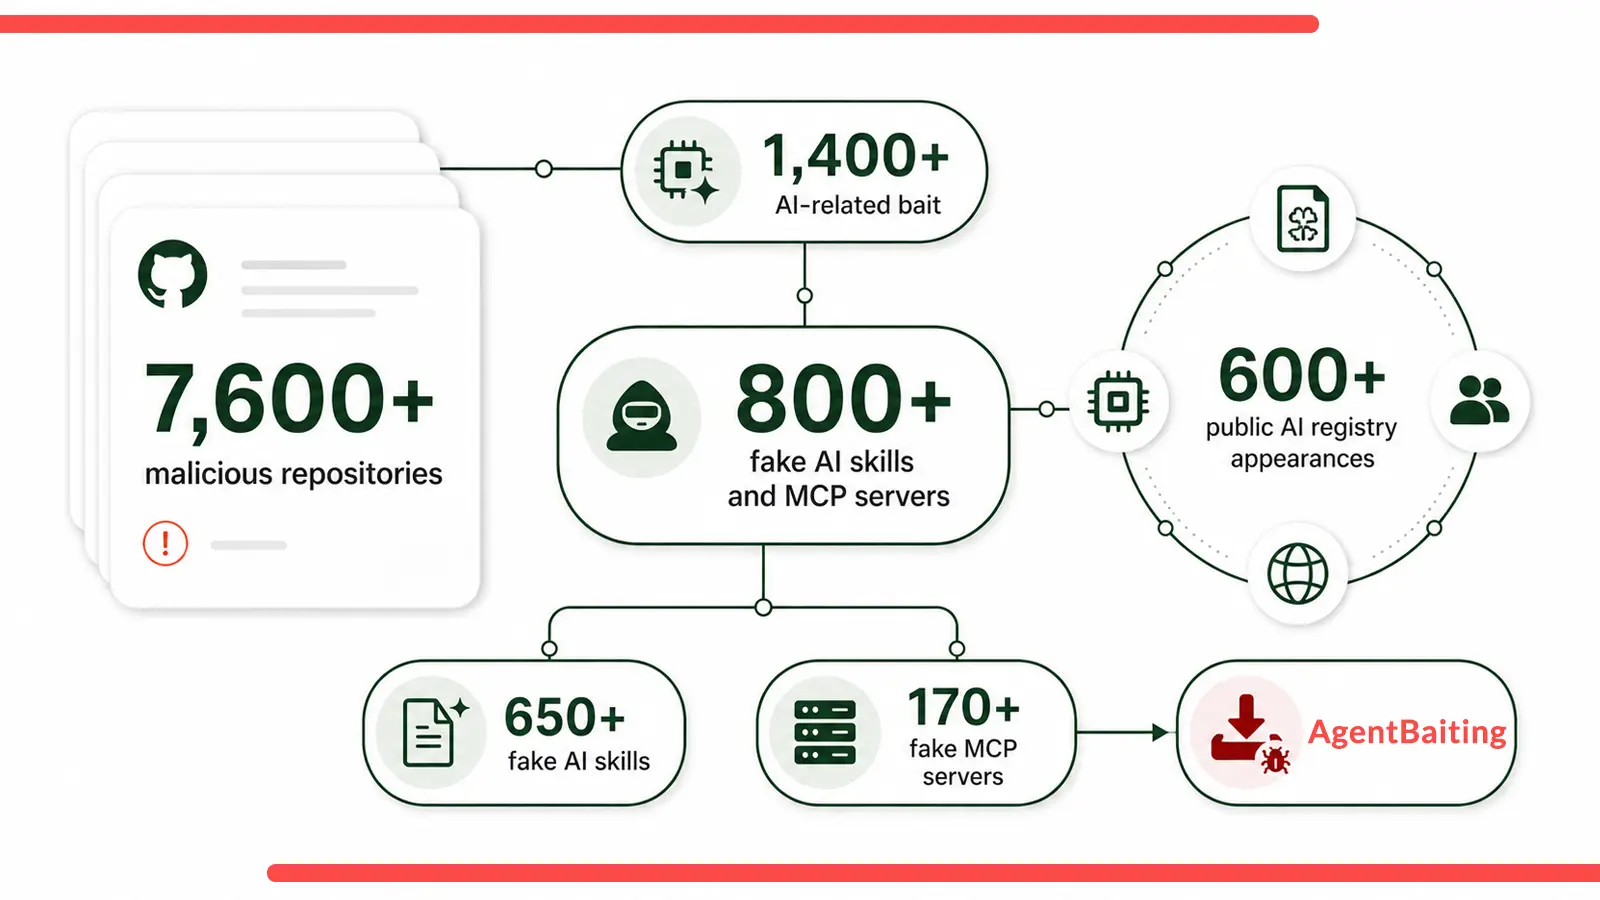
The rise of artificial intelligence has sparked a gold rush for developers and businesses alike, eager to integrate new “AI Skills” and Model Context Protocol (MCP) servers into their workflows. Unfortunately, cybercriminals are mirroring this enthusiasm to launch a widespread campaign known as “AgentBaiting.” By infiltrating legitimate-looking GitHub projects and public capability registries, these actors are baiting users into downloading what they believe are productivity-enhancing tools. In reality, these ZIP archives contain “SmartLoader” malware, marking a dangerous evolution in how malicious code is weaponized to exploit our growing reliance on AI-driven automation.
The scale of this operation is staggering, with security researchers uncovering over 7,600 malicious repositories linked to roughly 6,600 fraudulent profiles. These attackers do not rely on clumsy phishing emails; they invest significant effort in grooming their digital footprint, copying popular repositories, crafting professional-looking documentation, and maintaining a veneer of credibility. By posing as essential integrations for platforms like Claude, Databricks, or Docker, these campaigns successfully target both individual developers and enterprise systems. Once a user triggers the “installation” process, the script silently executes a payload designed to steal sensitive data, including login credentials and active browser sessions.
Perhaps the most alarming shift is how these malicious projects are now finding their way into the world. In the past, a victim had to click a malicious link or manually search for a specific file. Today, AI agents themselves—such as those powering Gemini, ChatGPT, or Claude Code—can autonomously discover these traps. When a user asks an AI to find a specific integration or plugin, the agent may independently search public directories and inadvertently suggest one of these compromised repositories. Even if the AI suggests legitimate alternatives, the inclusion of malicious “options” creates a direct, sanctioned pipeline for malware to enter a business environment.
This development fundamentally changes the risk model for organizations. Because the threat is no longer limited to human error or risky downloads, IT and security teams must treat every new AI-driven tool with extreme skepticism. Public registries, while useful, are currently proving to be a playground for threat actors who leverage the sheer volume of available code to obscure their malicious activity. Relying on “crowdsourced” or unverified tools allows attackers to piggyback on the trust users place in open-source platforms, turning a routine search for productivity into a potential compromise of an entire company’s intellectual property.
To combat this, professional organizations must move away from using unrestricted discovery methods. Security protocols should now mandate the use of curated, pre-approved catalogs for all AI Skills and plug-ins. Any new capability must be tested in a strictly isolated “sandbox” environment—distinct from production data, cloud credentials, or active SSH keys—to ensure it behaves as expected without hidden network callbacks. Most importantly, teams should train employees to identify the classic signs of a “fake” install: if a supposedly modern AI server comes in a standard ZIP file rather than a proper package manager installation, it should be rejected immediately.
Finally, firms must assume that a compromise is possible and act accordingly. If an endpoint is suspected of running SmartLoader, simple password resets are rarely sufficient, as the malware is designed to harvest live session tokens and persistent browser data. Security teams must treat the situation as a total identity breach, revoking all active OAuth grants, API tokens, and cloud credentials while isolating the affected host. As we lean further into the AI era, human vigilance remains our most critical defense; by verifying the source, vetting the code, and limiting the scope of our tools, we can ensure that our pursuit of innovation doesn’t inadvertently hand the keys to our digital infrastructure to those waiting in the shadows.